본문으로 건너뛰기

스스로 처리되는 서류 작업.

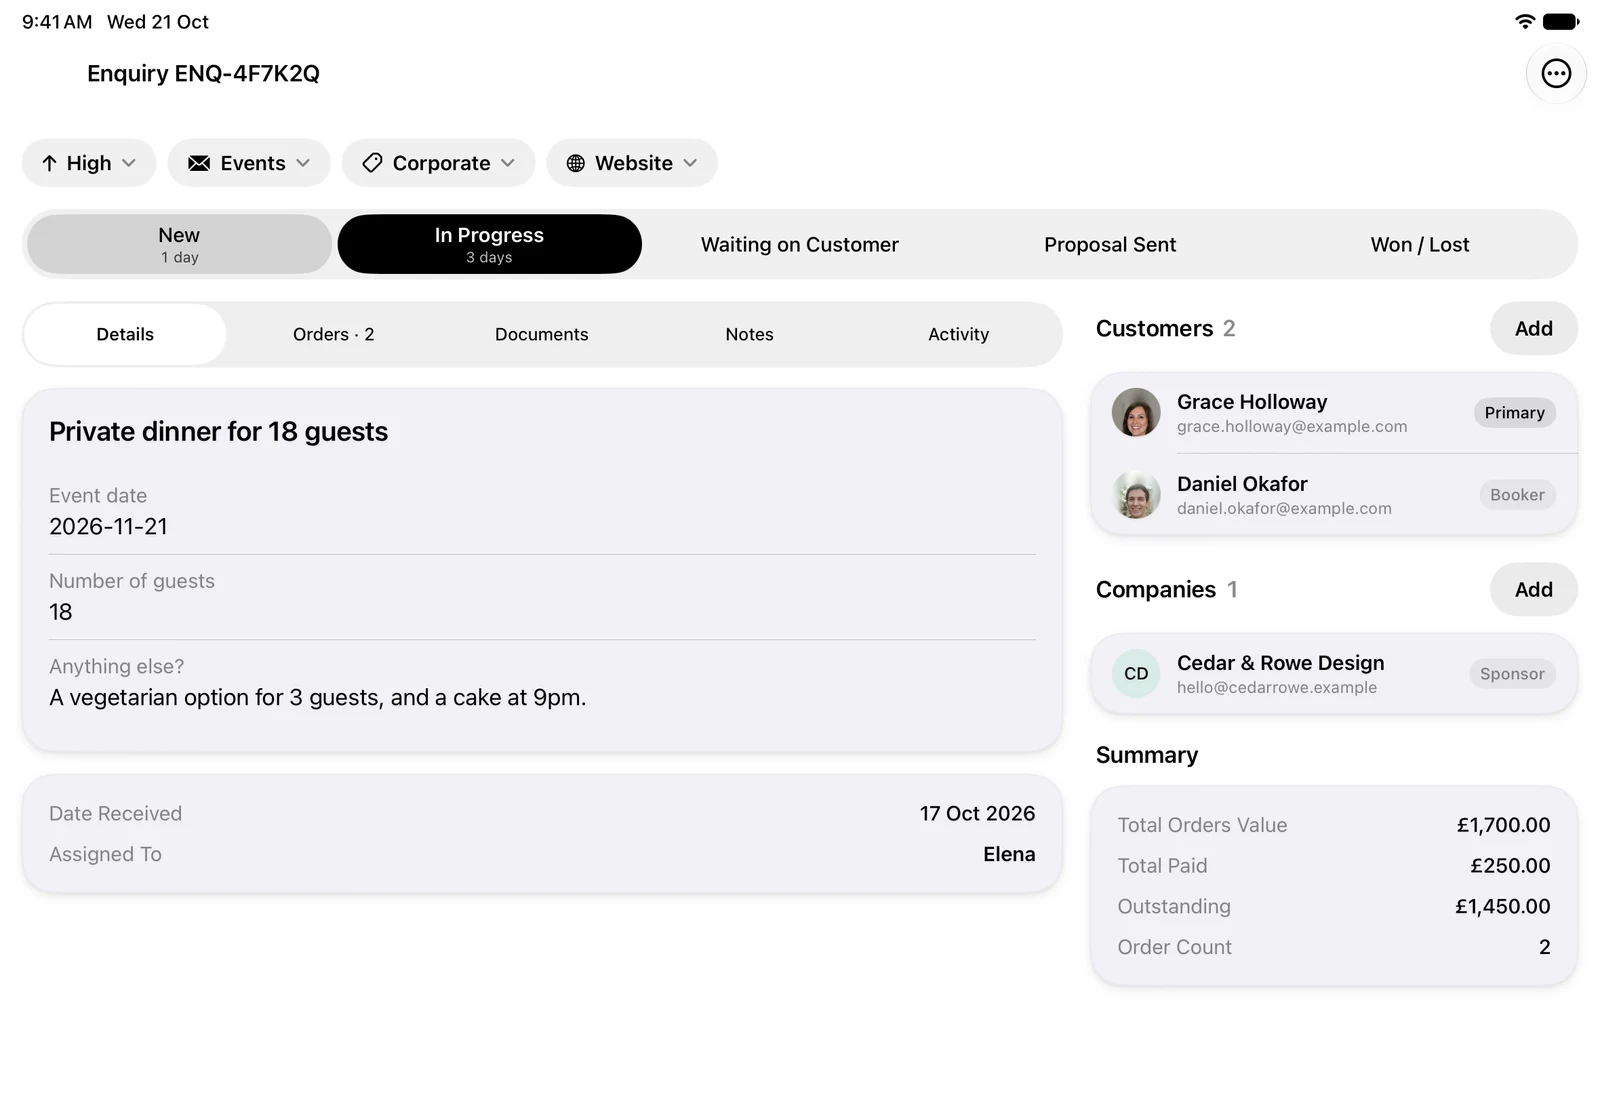
입력 항목, 파일, 사진, 서명과 결제 수단을 받는 다단계 양식과 문서를 만드세요. 답변을 고객 정보에 반영하고, 회원 신청이나 문의 처리 절차에 연결할 수 있습니다.
실무를 위한 양식.

  1. 01

    올바른 정보를 수집하는 접수 양식.

    고객이나 회원에게 필요한 질문을 단계별로 구성하세요. 방문, 클래스, 트리트먼트나 행사 전에 답변, 파일과 사진을 받을 수 있습니다.

  2. 02

    내장 서명이 포함된 면책 동의서 및 계약서.

    동의서와 서비스 계약서를 온라인으로 보내고, 전자 서명과 작성 시각, 완료 내역을 기록하세요.

  3. 03

    자동으로 트리거되며, 독촉할 필요 없음.

    예약 생성이나 일정 변경에 맞춰 필요한 양식과 계약서를 보내도록 설정할 수 있습니다.

종이는 줄이고, 보호는 강화.

자동 리마인더로 양식 완료율
최대
95%
사전 완료된 양식으로 체크인 시간 감소
최대
80%
양식이 안전하게 저장되고 즉시 검색 가능
최대
100%

올바른 기록에 보관.

문서

파일 업로드문서 만들기양식 만들기
스파 사전 문진표
2026년 10월 14일 제출 • 양식
작성 완료
멤버십 계약서
2026년 10월 15일 • 문서 • 2026년 10월 16일 서명
서명 완료
2/2 서명 완료Emma MorganLinden House
시술 동의서
2026년 10월 16일 • 문서 • emma@example.com(으)로 전송됨
서명 대기
0/1 서명 완료Emma Morgan
Passport.pdf
1.2 MB • 2026년 10월 2일 • 신분증
확인됨

고객 프로필에 저장.

고객 프로필에서 방문이나 지점별로 제출한 양식, 동의서와 계약서의 이력을 확인하세요.

문의와 기업에도 보관.

문서는 문의나 기업 계정에도 보관할 수 있어, 계약서가 해당 거래와 기업에 그대로 연결됩니다.

단일 정보 소스.

문서를 고객과 예약 기록에 연결해 Tiquo에서 함께 관리하세요.

유연한 로직, 완전한 제어.

  • 조건부 필드와 스마트 로직.

    앞선 답변에 따라 질문을 표시하거나 숨기세요. 고객에게 필요한 항목만 요청할 수 있습니다.

  • 서비스, 지점과 워크플로 규칙.

    서비스와 지점별로 필요한 양식을 지정하고, 예약 절차의 어느 단계에서 보낼지 설정하세요.

  • 권한 및 접근 제어.

    직원 역할에 따라 양식과 문서를 조회·수정·관리할 수 있는 권한을 설정하세요.

처음부터 안전하고 규정 준수.

  1. 발송됨
  2. 열람됨
  3. 서명됨
  4. 봉인됨

암호화된 저장 및 접근 제어.

모든 양식 데이터와 서명된 문서는 암호화되며 역할 기반 접근 제어로 보호됩니다.

감사 추적 및 이력.

문서를 보낸 시각과 작성·서명한 시각을 기록해 처리 이력을 확인할 수 있습니다.

규제 환경을 위해 구축.

동의서와 서비스 기록을 보관해야 하는 호텔, 웰니스 시설과 서비스업에서 사용할 수 있습니다.

자주 묻는 질문

종이는 줄이고, 보호는 강화.

© 2026 Tiquo. "Tiquo"와 Tiquo 로고는 Tiquo Ltd의 등록 상표입니다.

GDPR · CCPA · PCI DSS · ICO · Cyber Essentials Certified · EU–US DPF · SOC 2 Type II (in progress) · ISO 27001 (in progress)

Security & Operational

  • 99.99% SLA Uptime
  • AES-256 encryption at rest
  • TLS 1.3 in transit
  • AES-256 / TLS 1.3
  • Perfect Forward Secrecy (PFS)
  • HTTP Strict Transport Security (HSTS)
  • 99.999999999% (11 nines) data durability
  • Automated backups
  • DDoS protection
  • Web Application Firewall (WAF)
  • Zero Trust posture
  • Role-Based Access Control (RBAC)
  • Principle of Least Privilege
  • Secret scanning in CI
  • SBOM generation
  • Dependency supply-chain controls
  • 24/7 infrastructure monitoring
  • GDPR Article 22 safeguards
  • Data Protection Impact Assessments (DPIAs)
  • Records of Processing Activities (ROPA)
  • SAML 2.0 SSO
  • EASIE SSO
  • OAuth 2.0 / OpenID Connect (OIDC)
  • SCIM 2.0 provisioning
  • MFA / 2FA enforcement
  • Responsible disclosure / bug bounty programme

Privacy, Data Protection & Statutory Obligations

  • ICO Registered
  • UK Modern Slavery Act 2015 compliant
  • UK Public Interest Disclosure Act 1998 compliant
  • EU Article 27 Representative appointed (Paris, France)
  • Swiss FADP Article 14 Representative appointed
  • UK GDPR compliant
  • EU GDPR/DSGVO compliant
  • UK Data Protection Act 2018 compliant
  • Swiss revFADP compliant
  • CCPA / CPRA compliant (California)
  • VCDPA compliant (Virginia)
  • CPA compliant (Colorado)
  • CTDPA compliant (Connecticut)
  • TDPSA compliant (Texas)
  • OCPA compliant (Oregon)
  • MCDPA compliant (Montana)
  • FDBR compliant (Florida)
  • ICDPA compliant (Iowa)
  • ICDPA compliant (Indiana)
  • TIPA compliant (Tennessee)
  • DPDPA compliant (Delaware)
  • NJDPA compliant (New Jersey)
  • NHDPA compliant (New Hampshire)
  • NDPA compliant (Nebraska)
  • MCDPA compliant (Minnesota)
  • MODPA compliant (Maryland)
  • KCDPA compliant (Kentucky)
  • RIDTPPA compliant (Rhode Island)
  • Canada PIPEDA compliant
  • Quebec Law 25 compliant
  • Alberta PIPA compliant
  • British Columbia PIPA compliant
  • Singapore PDPA compliant
  • Hong Kong PDPO compliant
  • Brazil LGPD compliant
  • Japan APPI compliant
  • Australia Privacy Act / APPs compliant
  • India DPDPA 2023 compliant
  • Thailand PDPA compliant
  • Malaysia PDPA 2010 (as amended 2024) compliant
  • New Zealand Privacy Act 2020 compliant
  • South Africa POPIA compliant
  • UAE PDPL compliant
  • Mexico LFPDPPP compliant
  • Kenya Data Protection Act 2019 compliant
  • Ghana Data Protection Act 2012 compliant
  • Nigeria NDPA 2023 compliant
  • Indonesia PDP Law 2022 compliant
  • Philippines Data Privacy Act 2012 compliant

Global Fiscal & E-Invoicing

  • EN 16931 - EU e-invoicing core standard
  • UBL 2.1 - Universal Business Language
  • Austria - RKSV
  • Belgium - Peppol BIS 3.0 (B2B)
  • Czechia - fiscalization
  • Croatia - Fiscalization 2.0
  • Denmark - Peppol BIS 3.0 (B2B)
  • France - NF525 / LNE / Infocert, Factur-X / PDP, E-Reporting
  • Germany - KassenSichV / TSE, DSFinV-K, GoBD, E-Rechnung B2B (XRechnung / ZUGFeRD)
  • Hungary - Online Szamla
  • Italy - Scontrino, FatturaPA (via SDI)
  • Lithuania - i.SAF / i.MAS
  • Norway - Peppol BIS 3.0 (B2B), SAF-T
  • Poland - KSeF
  • Portugal - ATCUD/QR, SAF-T PT
  • Slovakia - eKasa
  • Slovenia - fiscalization (davcno potrjevanje)
  • Spain - FacturaE, SII, VeriFactu, TicketBAI
  • Sweden - SKVFS (certified cash registers)
  • Argentina - ARCA (Q4 2026)
  • Australia - Peppol PINT A-NZ (Q4 2026)
  • Brazil - NFe, NFCe, NFSe (Q4 2026)
  • Chile - SII Chile (Q4 2026)
  • Colombia - DIAN (Q4 2026)
  • Finland - Finvoice, TEAPPSXML (Q4 2026)
  • Japan - JP PINT (Peppol) (Q3 2026)
  • Malaysia - Peppol Malaysia (Q4 2026)
  • Mexico - CFDI (Q4 2026)
  • New Zealand - Peppol PINT A-NZ (Q4 2026)
  • Peru - SUNAT (Q4 2026)
  • Romania - Peppol (RO e-invoice) (Q4 2026)
  • Saudi Arabia - ZATCA (Q4 2026)
  • Singapore - Peppol BIS 3.0 (Q4 2026)
  • United Arab Emirates - Peppol (5C) (Q4 2026)

Standards & Frameworks

  • Cyber Essentials Certified
  • SOC 2 Type II - audit in progress
  • ISO/IEC 27001 - audit in progress
  • NIST Cybersecurity Framework - aligned
  • NIST Privacy Framework - aligned
  • NIST SP 800-53 / 800-63 / 800-63B - aligned
  • NIST AI Risk Management Framework - aligned
  • CIS Critical Security Controls / CIS Benchmarks - aligned
  • OWASP ASVS & OWASP Top Ten - aligned
  • ISO 25010 (quality) - aligned
  • ISO 31000 (risk) - aligned
  • ITIL - aligned
  • W3C Web Standards - aligned
  • OpenAPI Standard - aligned
  • DevSecOps practices - aligned
  • ePrivacy Directive - aligned
  • EU Whistleblowing Directive (2019/1937) - aligned

Payments Compliance

  • PCI DSS Level 1
  • PSD2 / Strong Customer Authentication
  • 3D Secure (3DS)
  • EMVCo Level 1 & 2
  • AML / KYC controls
  • Sanctions screening (OFAC, UN, EU, HMT)

International Data Transfer Mechanisms

  • EU-US Data Privacy Framework
  • EU Standard Contractual Clauses (Decision 2021/914) - Modules 2 & 3
  • UK International Data Transfer Agreement (IDTA) + ICO Addendum
  • Swiss FDPIC-recognised transfer mechanisms
  • APEC Cross-Border Privacy Rules (CBPR)

Accessibility Compliance

  • ADA (Americans with Disabilities Act) - aligned
  • European Accessibility Act (EAA) 2025 - aligned
  • WCAG 2.2 - aligned
  • EN 301 549 - aligned
  • WAI-ARIA - aligned

숙박, 스파, 클래스, 이벤트, 식당 운영을 한곳에서.

Tiquo Ltd
런던, 영국

LinkedInTop Performer Spring

쿠키를 사용합니다

분석 및 광고용 쿠키를 허용할지 선택해 주세요. 동의하거나 거부할 수 있으며, 이 안내를 닫으면 거부한 것으로 처리됩니다.

자세히 알아보기