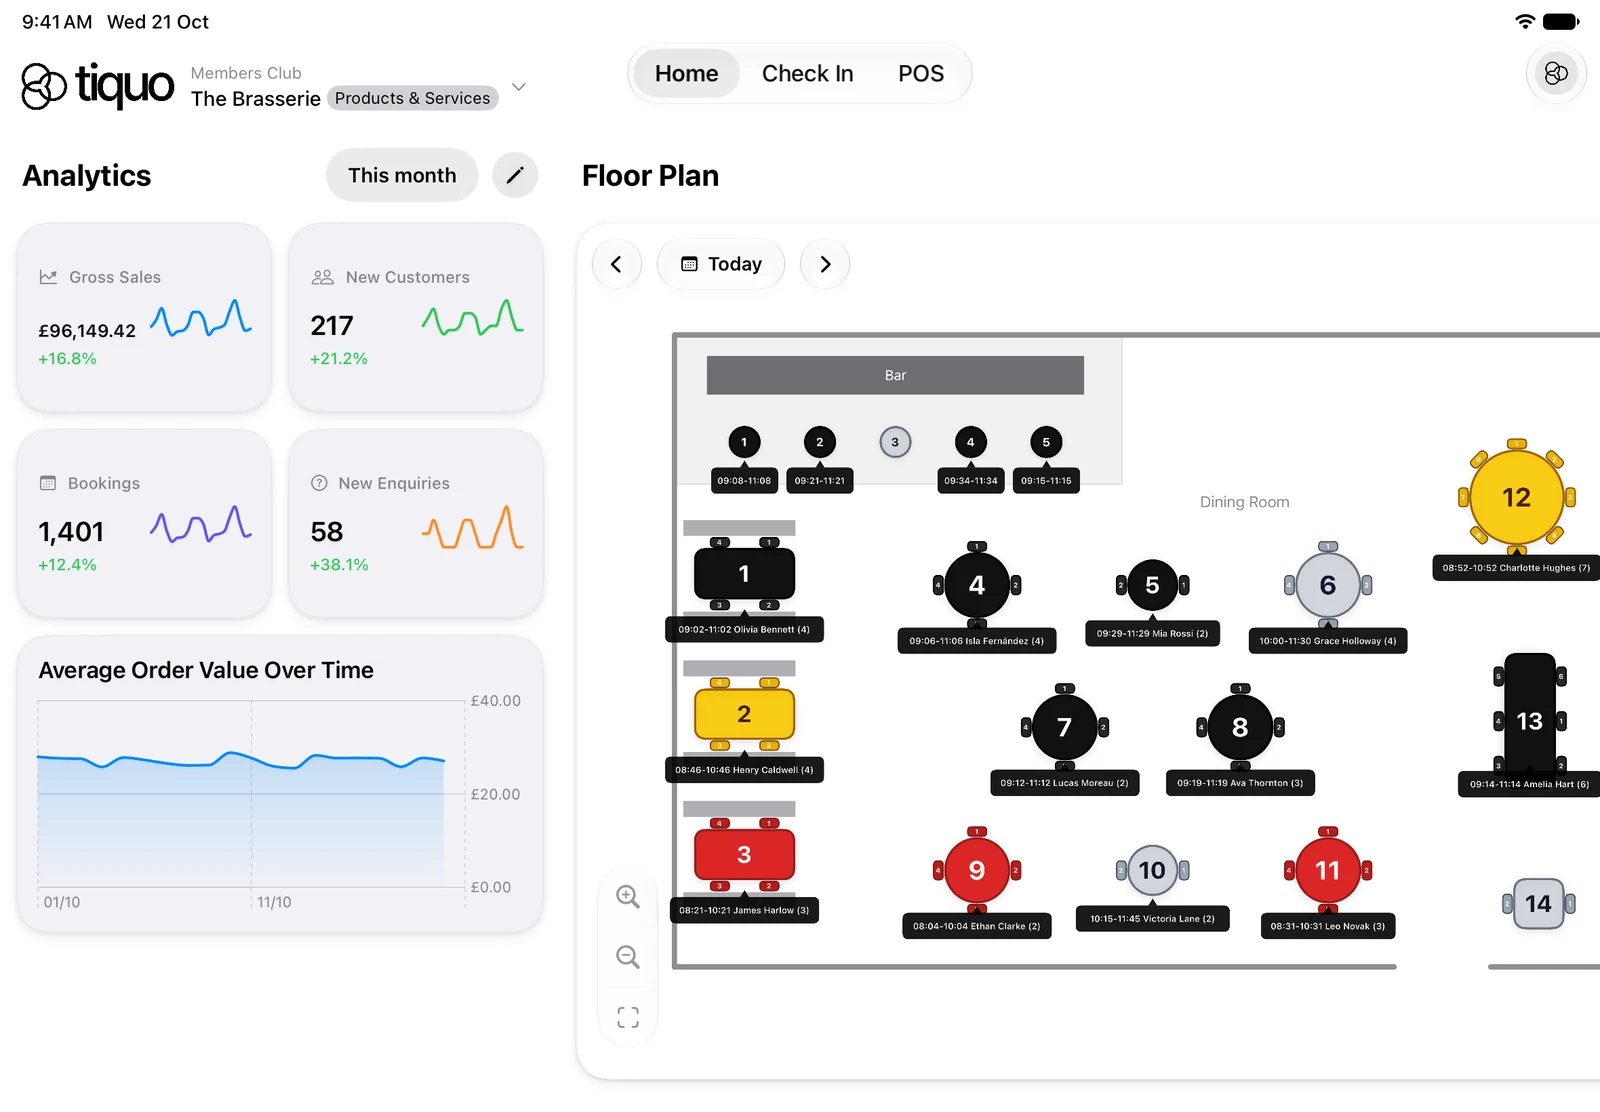
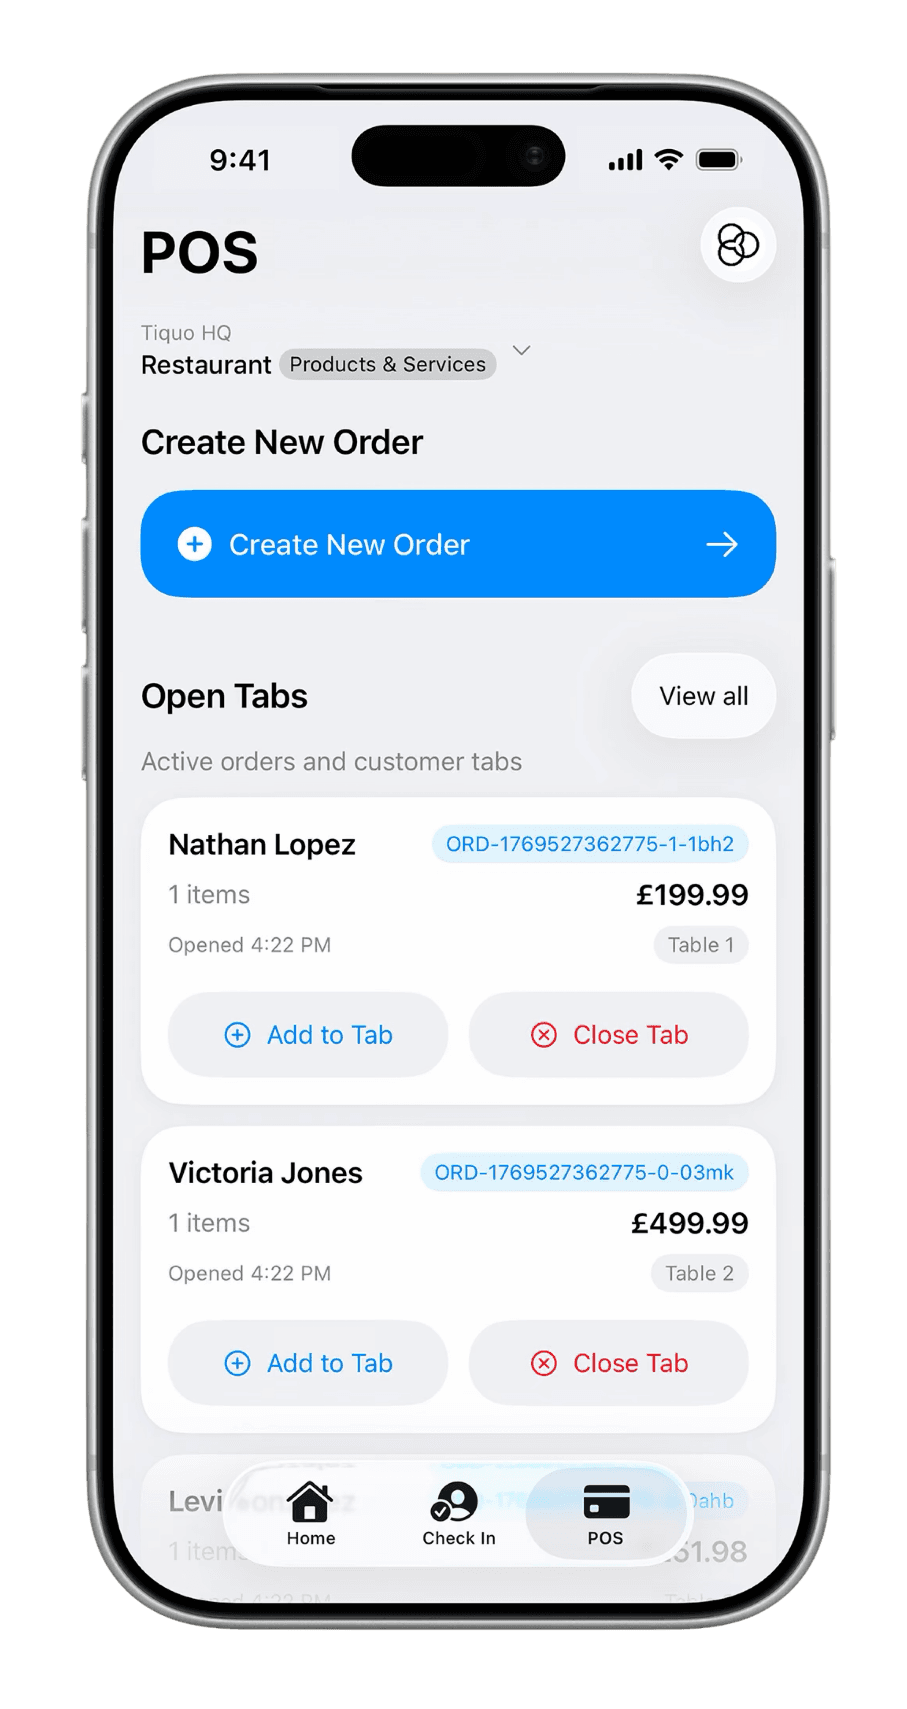
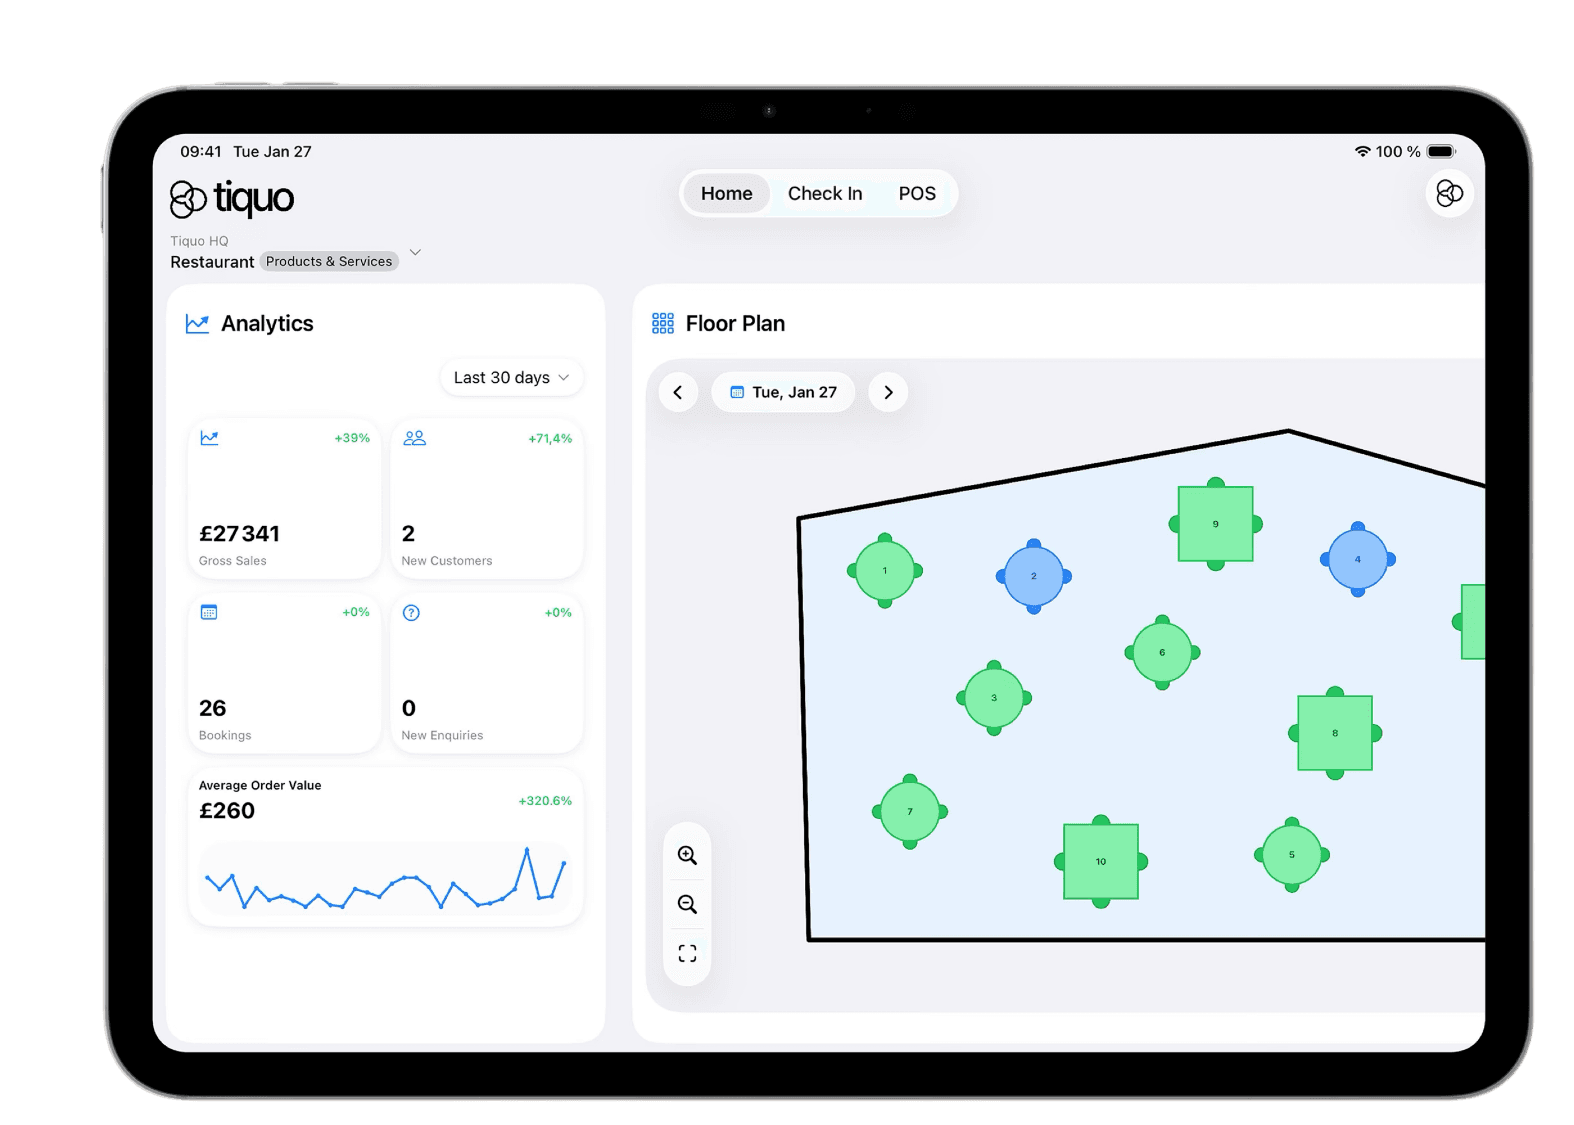
One unified platform for your entire operation.

POS and orders, products and inventory, bookings, payments, customers and companies, memberships, enquiries, forms, marketing, automation and analytics brought together in one configurable operating platform.

Everything, connected.

Unified data, unified experience.

Actions in Tiquo update instantly across the platform. A booking triggers a payment, a payment updates a membership, and both feed into reporting. Teams share the same records without having to sync or reconcile them manually.

Built for real-world operations.

Set up workflows around how your team handles treatments, classes, dining, rooms, packages and experiences.

Scales with your business, not in complexity.

Add locations, departments, services or new business models without rebuilding your system. Your operations, data and reporting stay connected as you grow.

Designed for staff adoption, not just dashboards.

Tiquo runs in the cloud, with a fast, clear interface for everyday work. Teams can learn it quickly and make fewer mistakes, with less training and fewer workarounds.

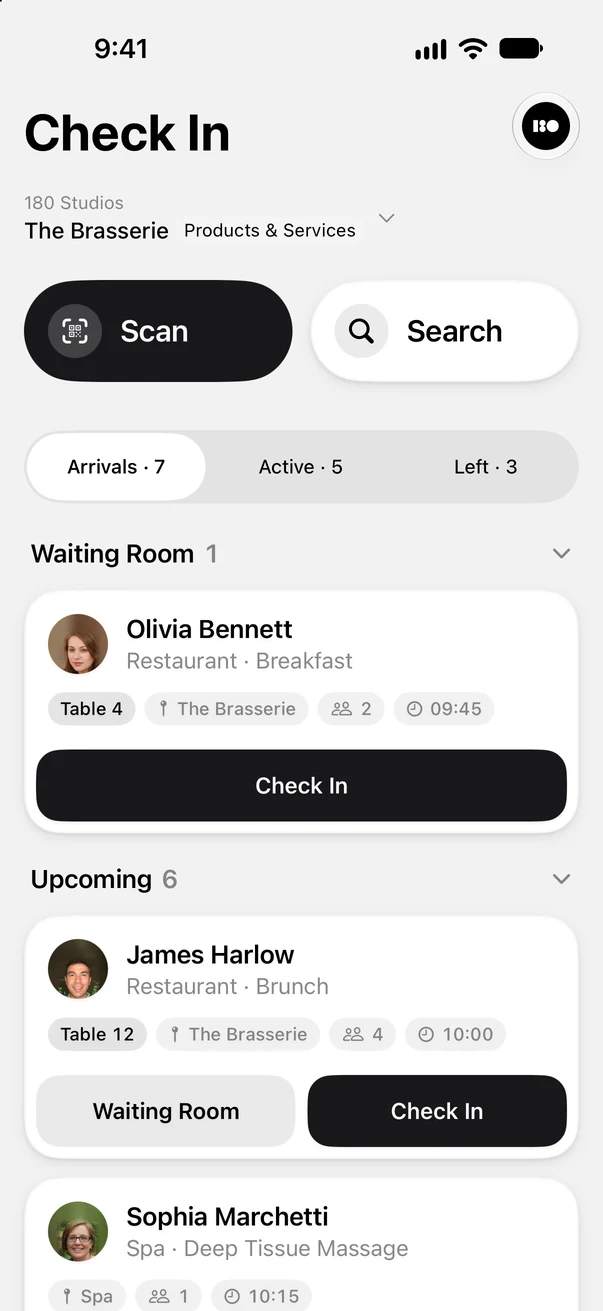
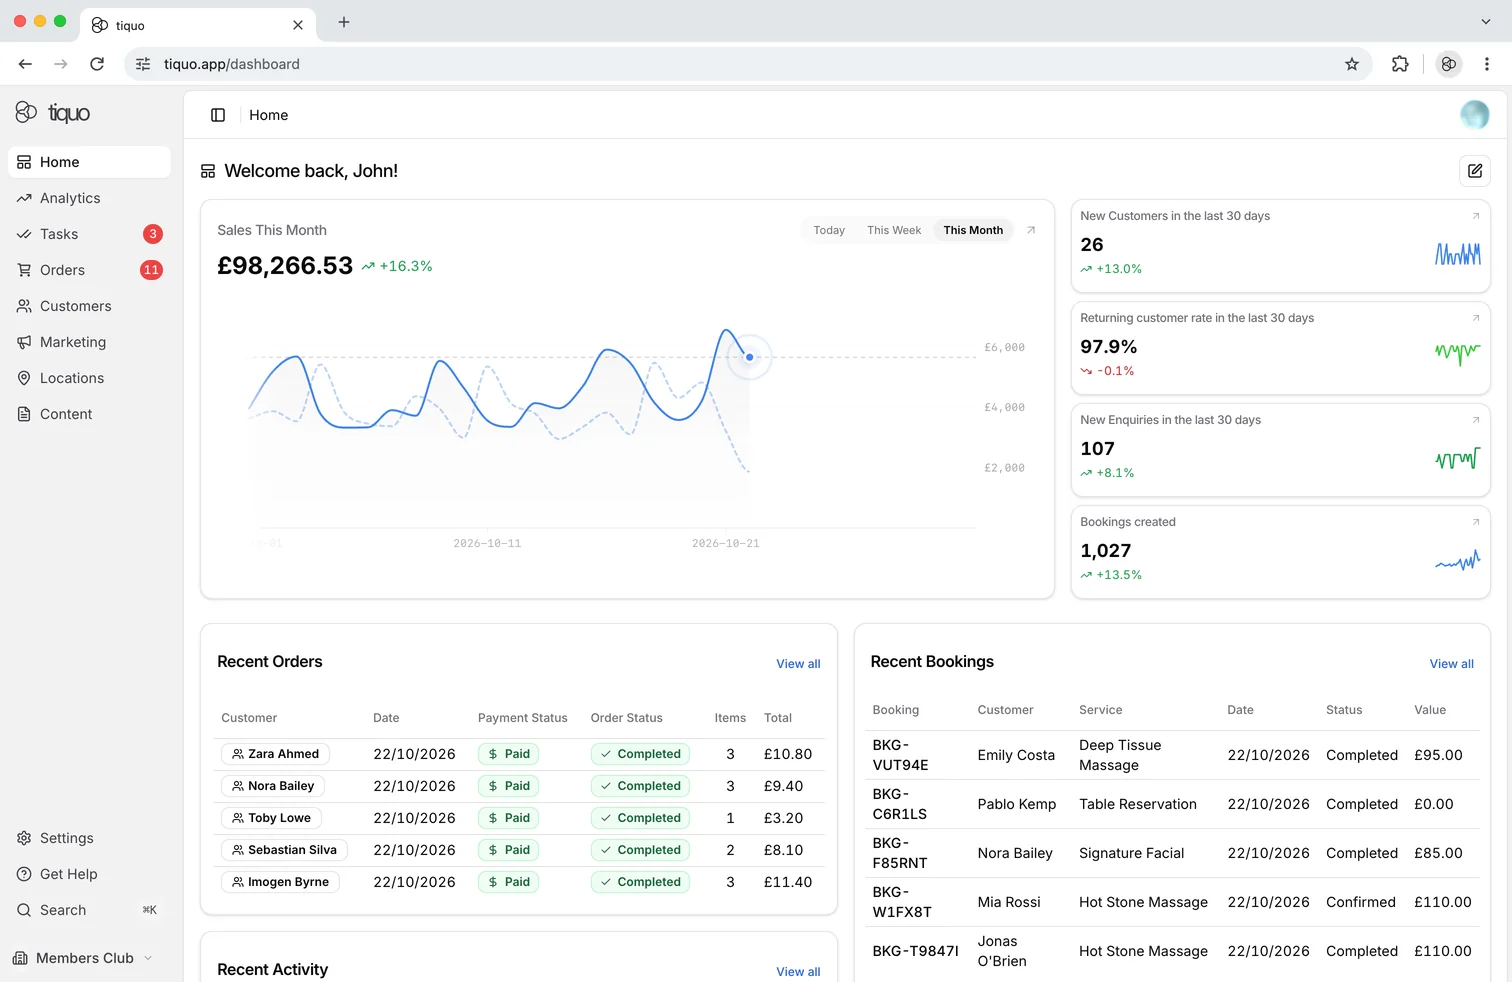
Tiquo on iphoneTiquo on ipad
tiquo.app/dashboard

Six modules. One customer record.

Bookings, payments, memberships, forms and reporting share the same live data, so every visit, spend and signature lands on one guest profile instead of six.

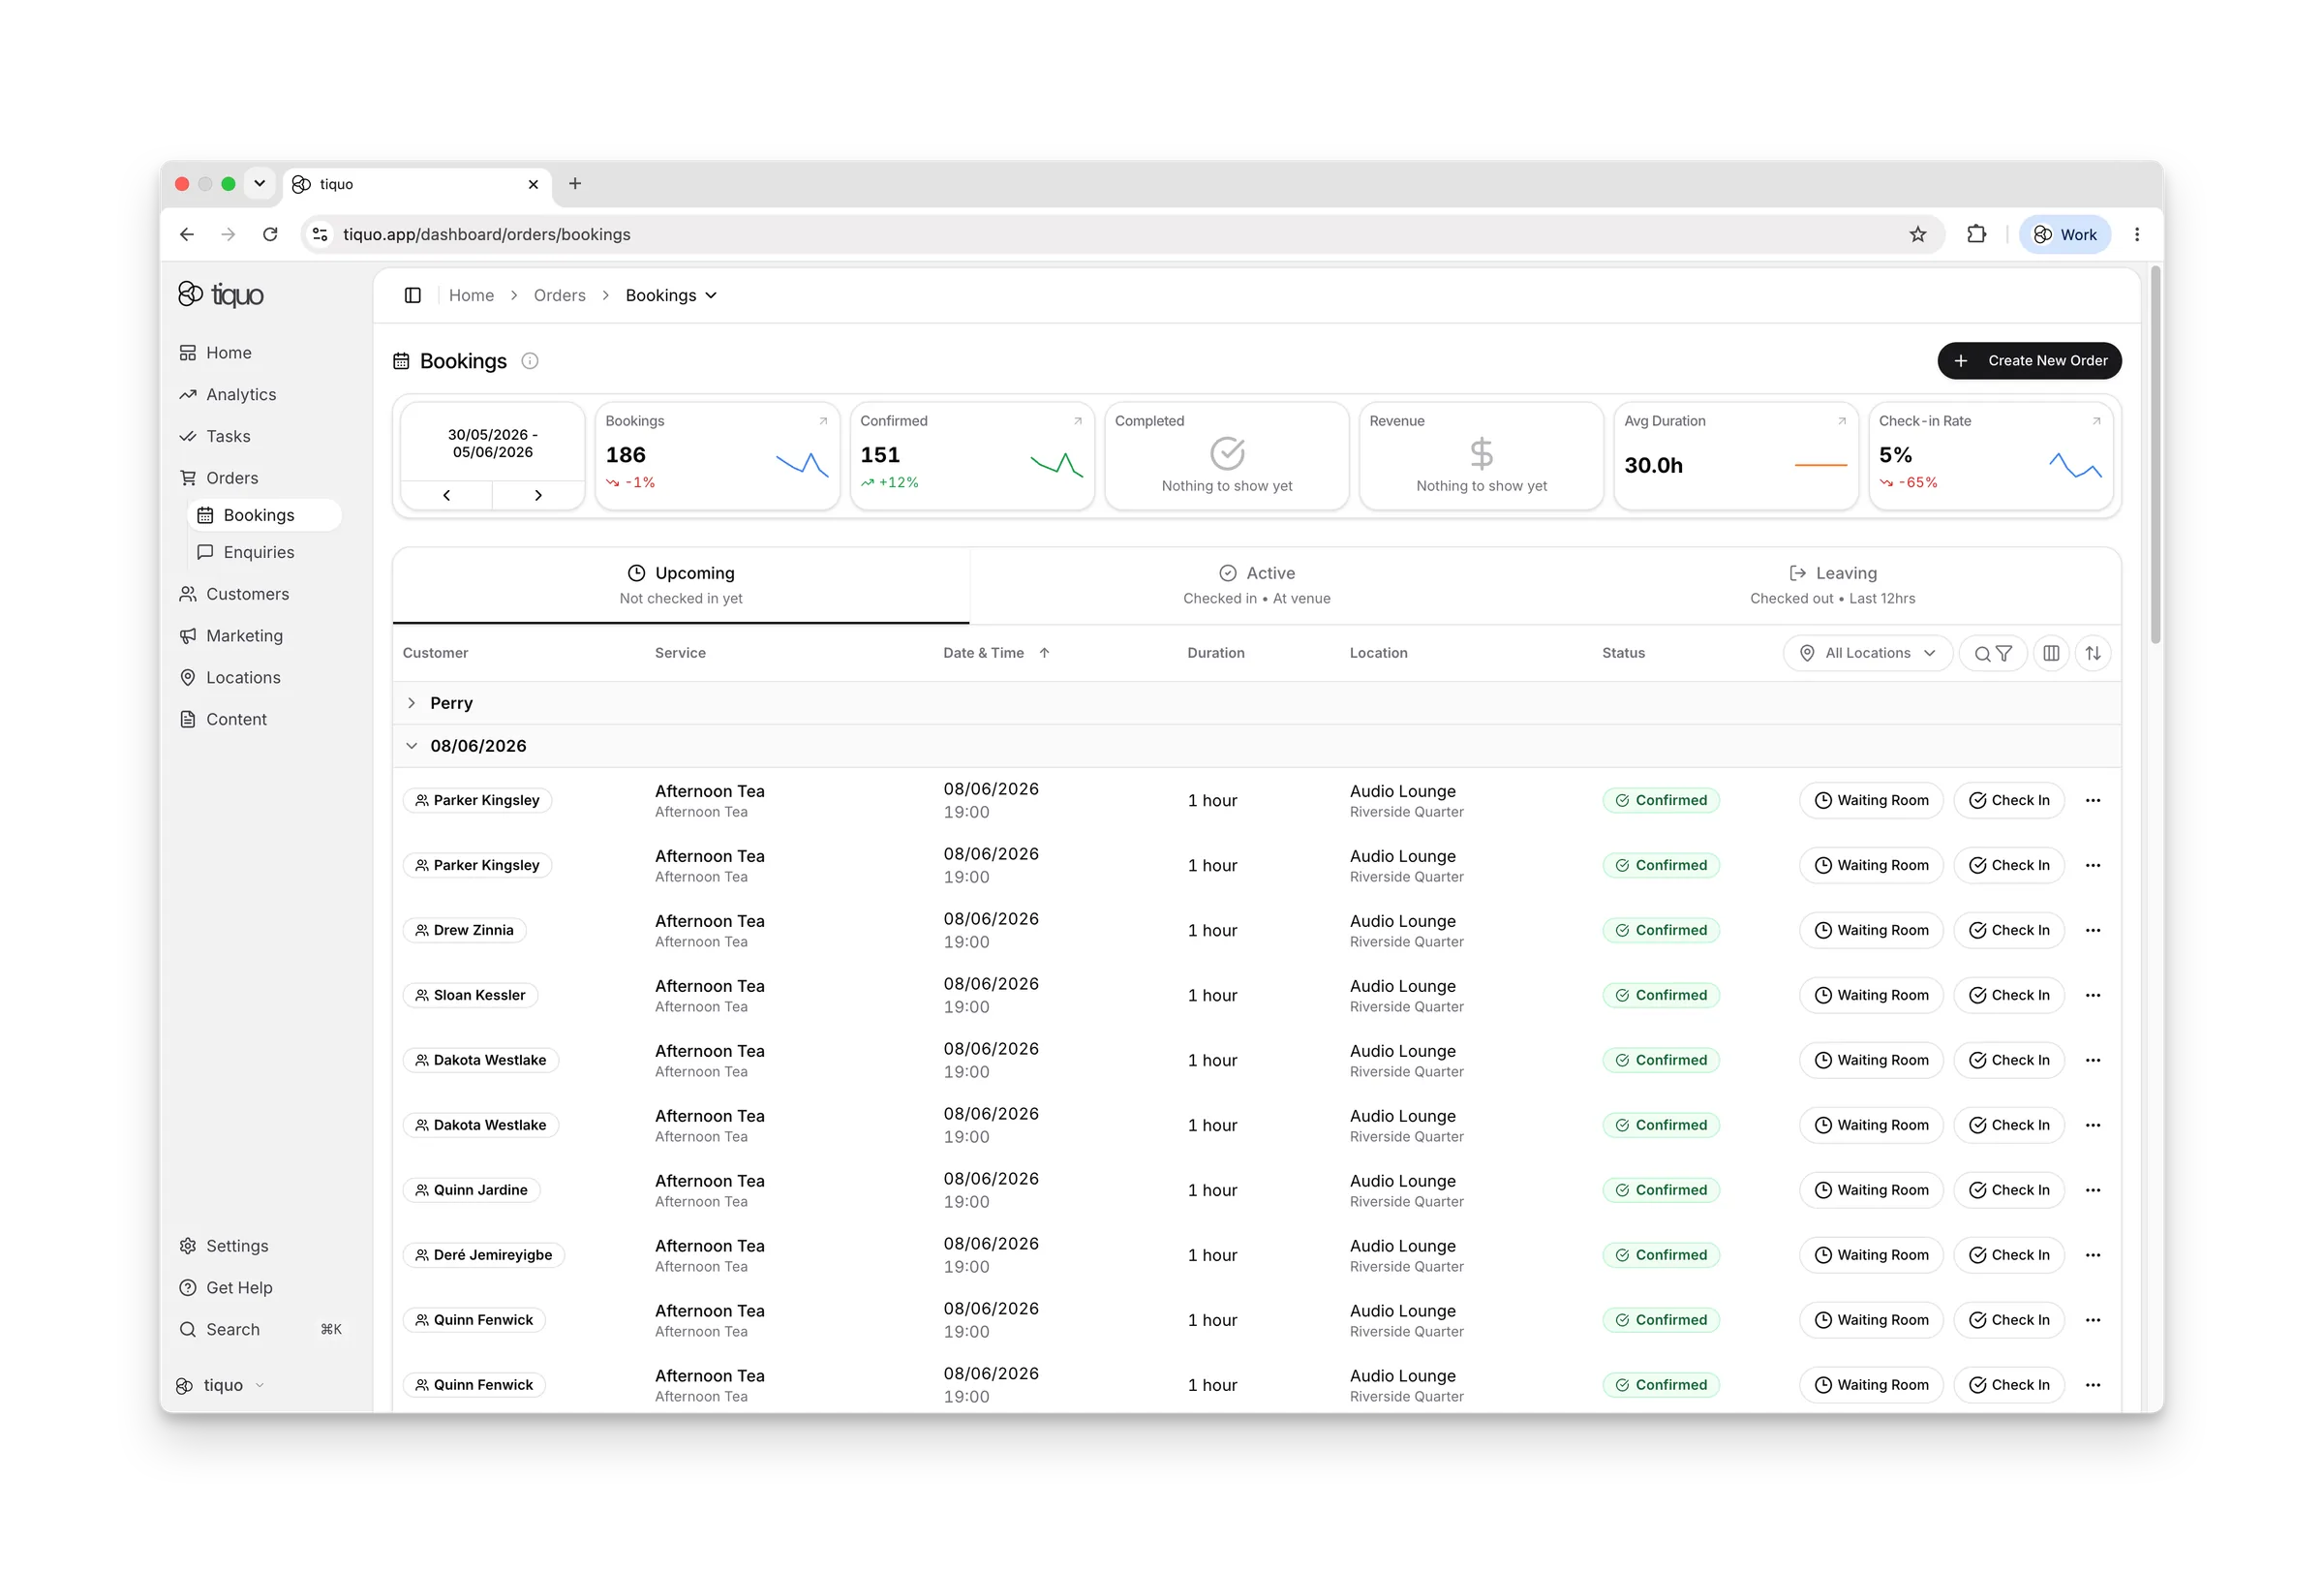
The Tiquo bookings list with today's confirmed bookings and check-in actions

Bookings

Rooms, tables, treatments and classes on one live calendar.

Availability checks staff, rooms and equipment as you book, so double bookings and whiteboard juggling disappear.

  • Live floor plans and tables
  • Walk-ins and waitlists
  • Packages, classes and events
  • Deposits taken at booking
  • Booking pages in 30+ languages
  • One-scan check-in on iPad or iPhone
Learn more
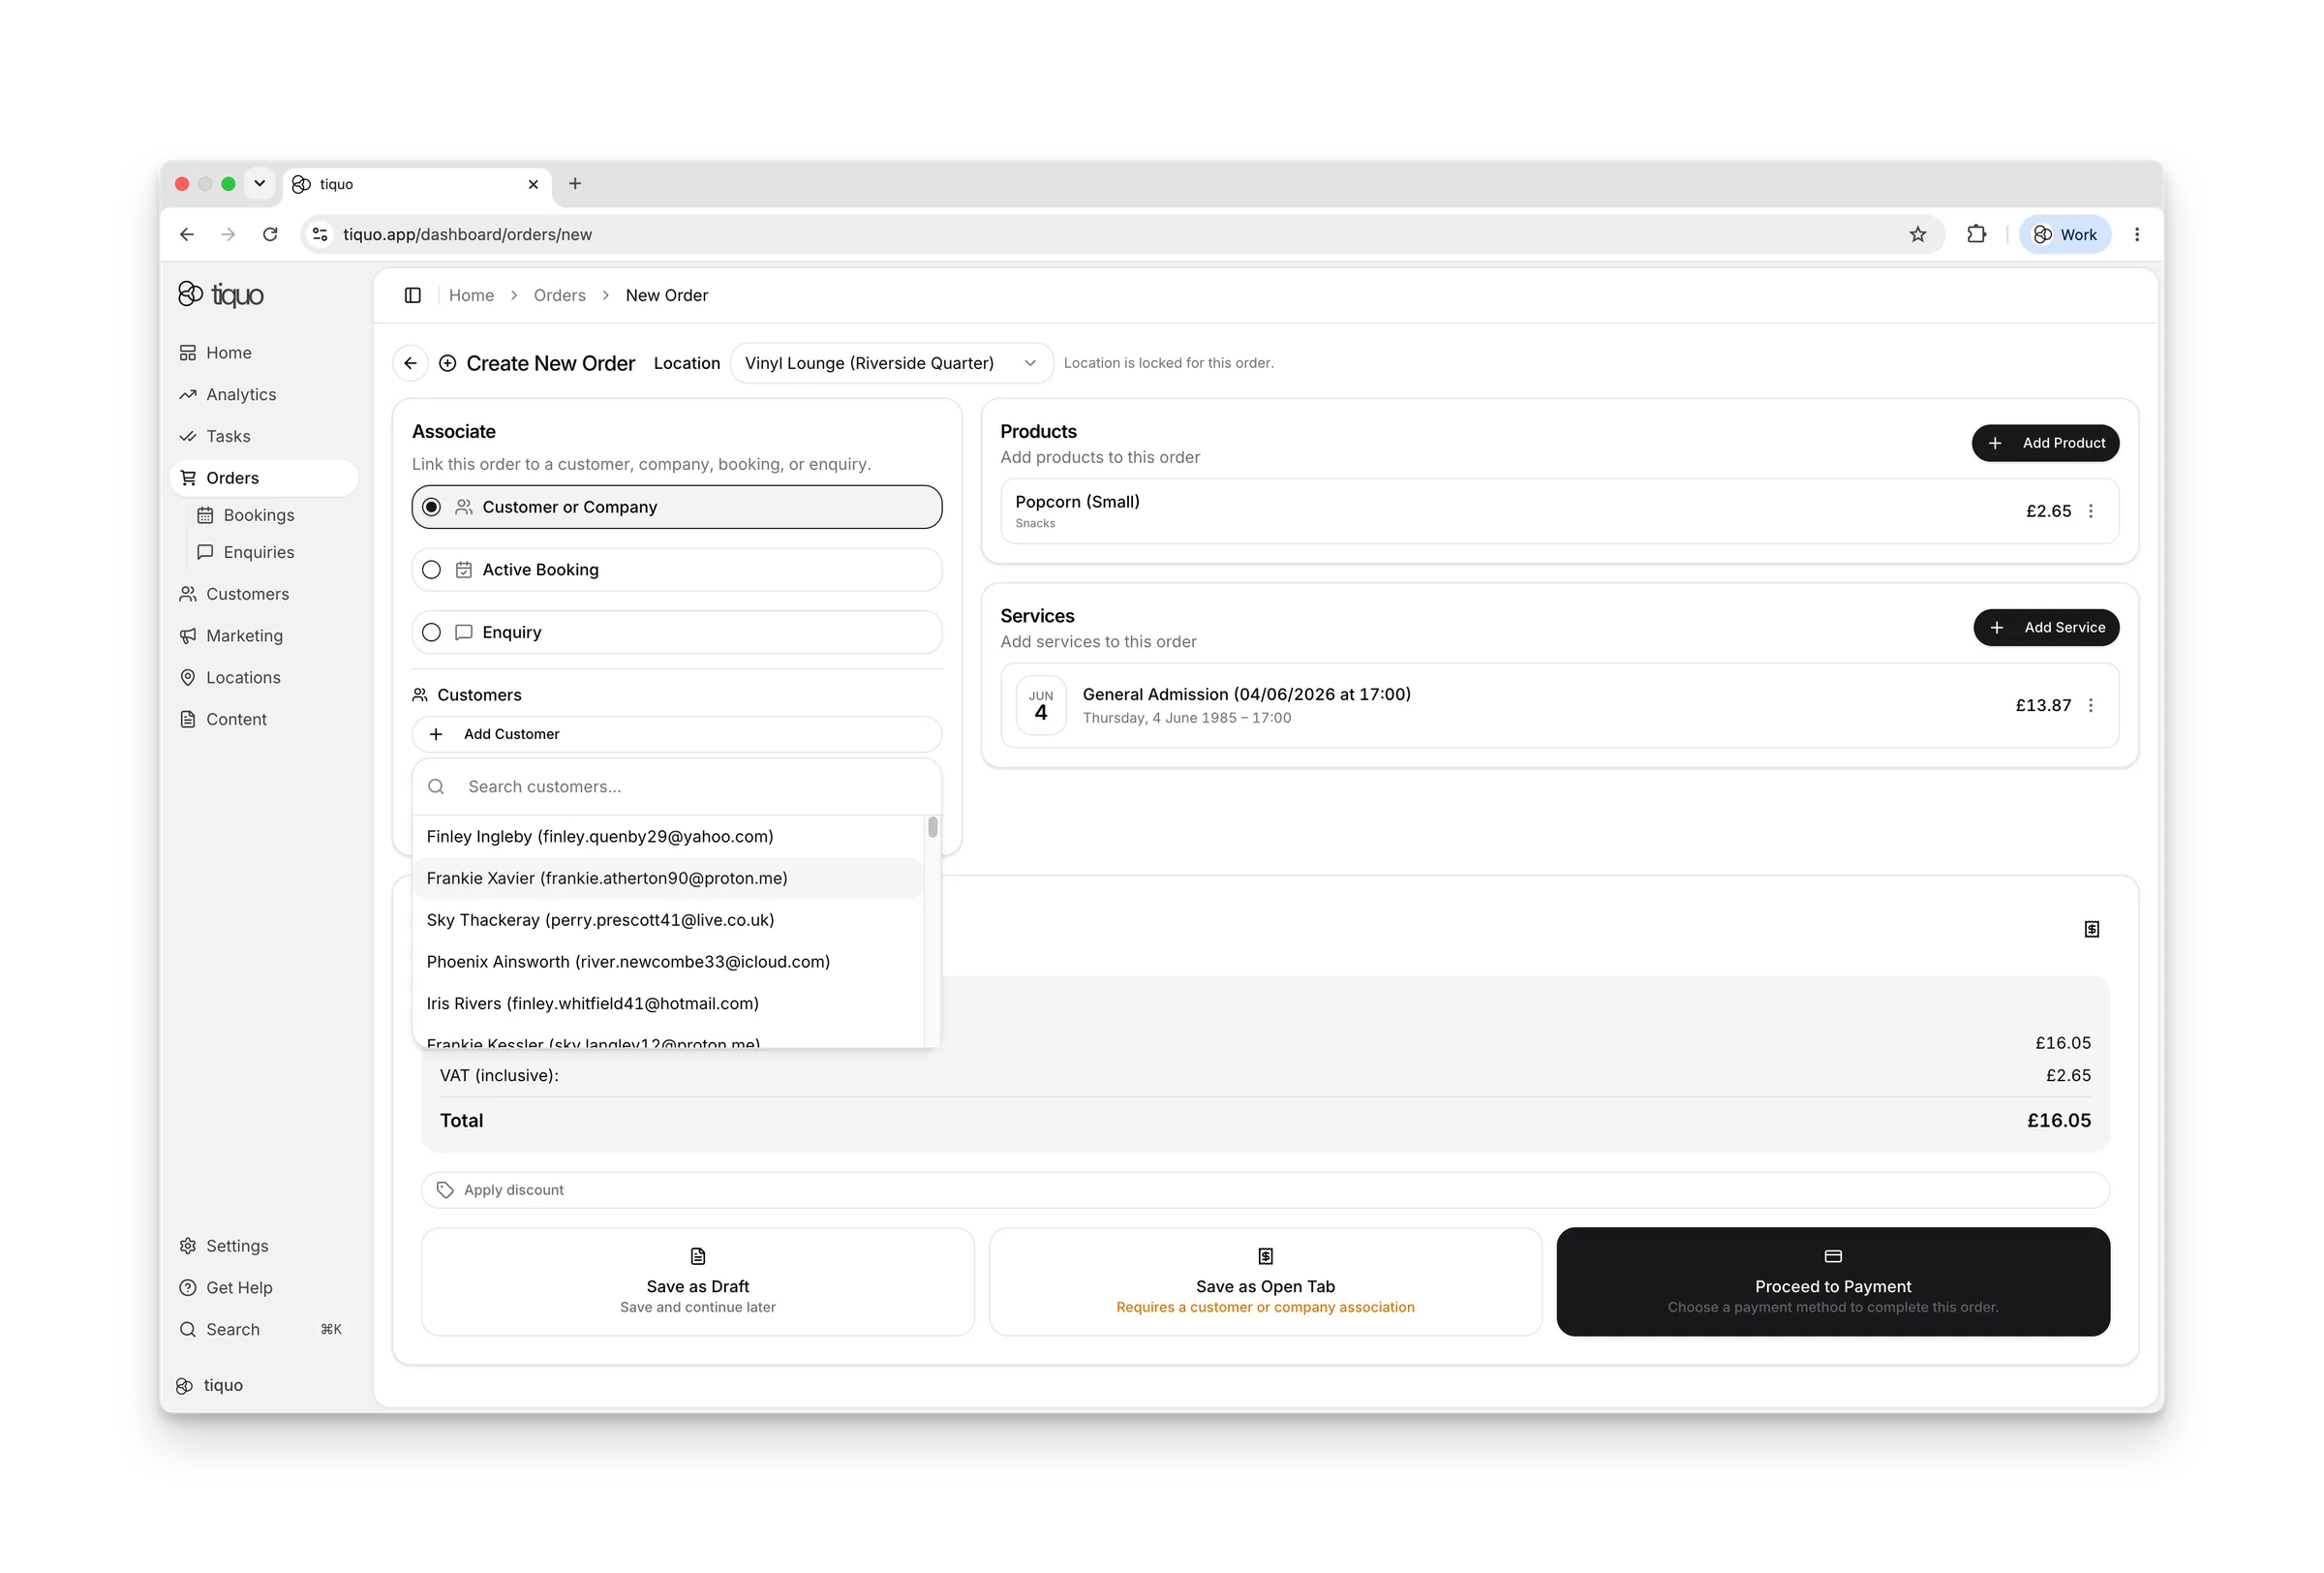
A new order in Tiquo linked to a customer, with products, services and payment

Payments

Every payment tied to its guest, order and booking.

Take payment at the counter, at the table or online, and Tiquo records it against the right customer and reconciles it for finance.

  • Tap to Pay and card terminals
  • Apple Pay, Google Pay and Klarna
  • Stored credit and wallet top-ups
  • Automatic payout reconciliation
  • Split bills by item, guest or amount
  • Open tabs, deposits and saved cards
Learn more
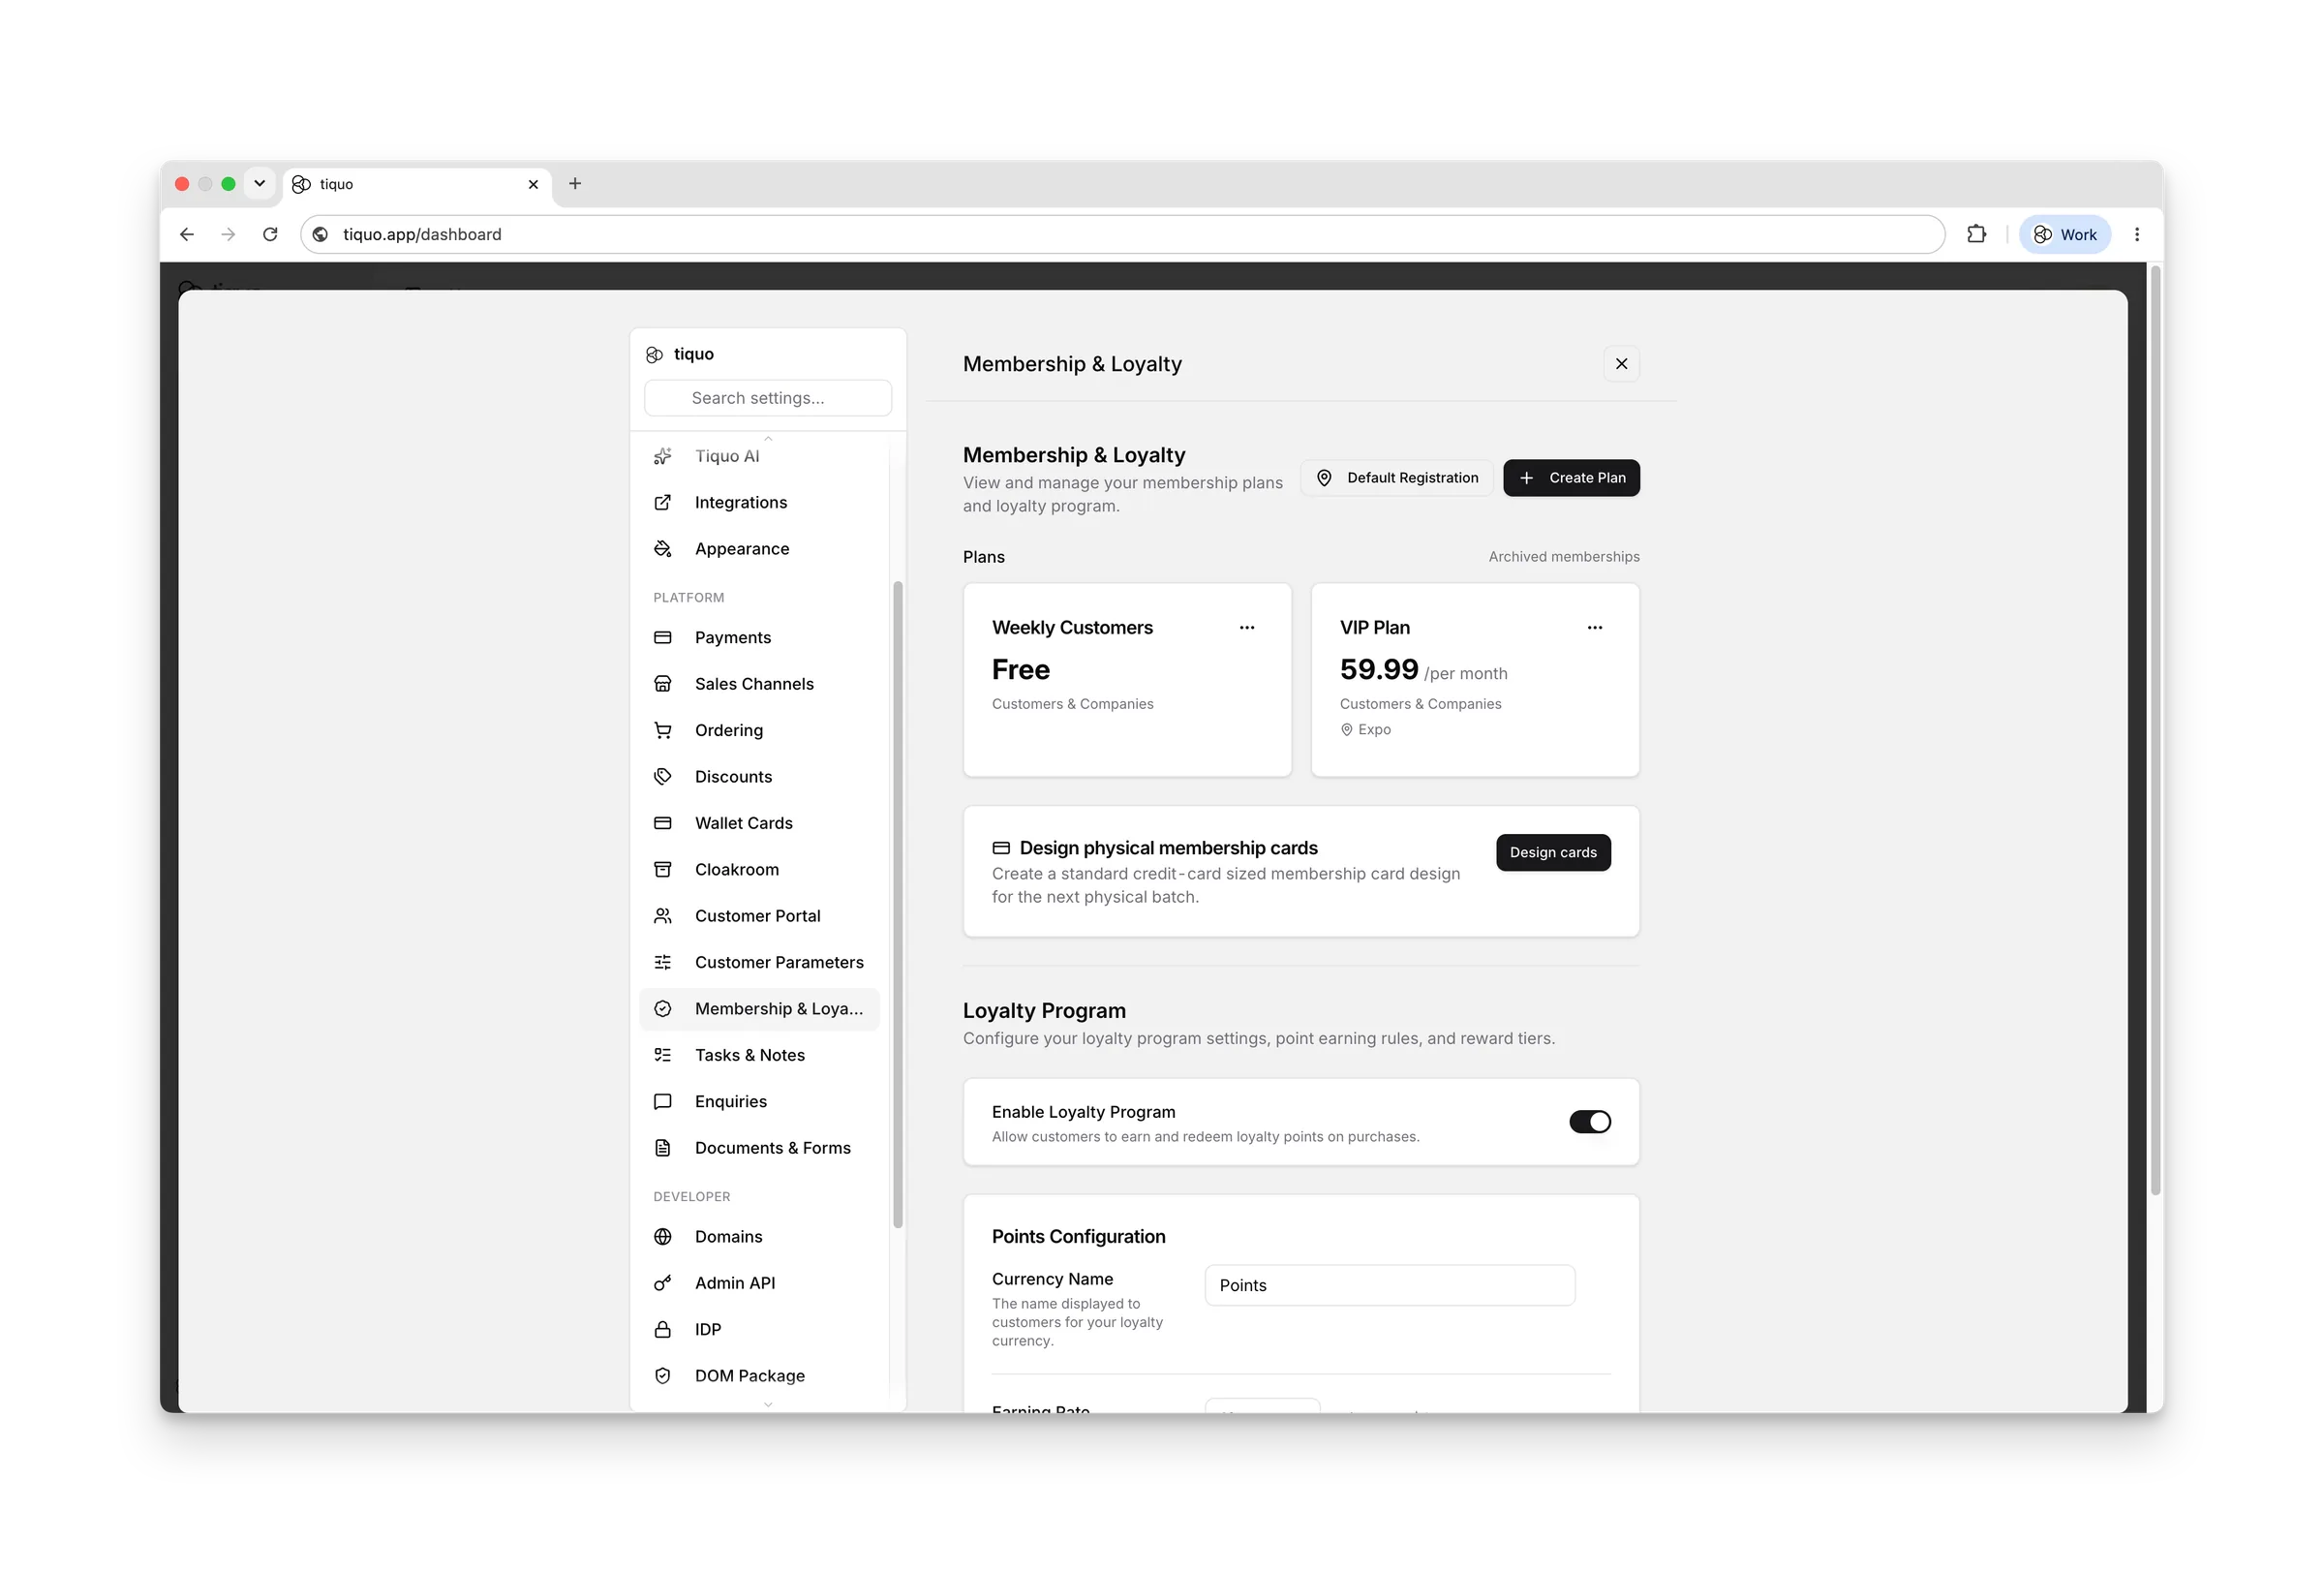
Tiquo membership and loyalty settings with plans and a points program

Memberships

Memberships, passes and loyalty that run themselves.

Sell individual and company plans with trials and joining fees, then let renewals, benefits and rewards take care of themselves.

  • Apple and Google Wallet cards
  • Guest and access passes
  • Loyalty points and stored credit
  • Card or direct debit billing
  • Company plans with several members
  • Trials, joining fees and pricing
Learn more
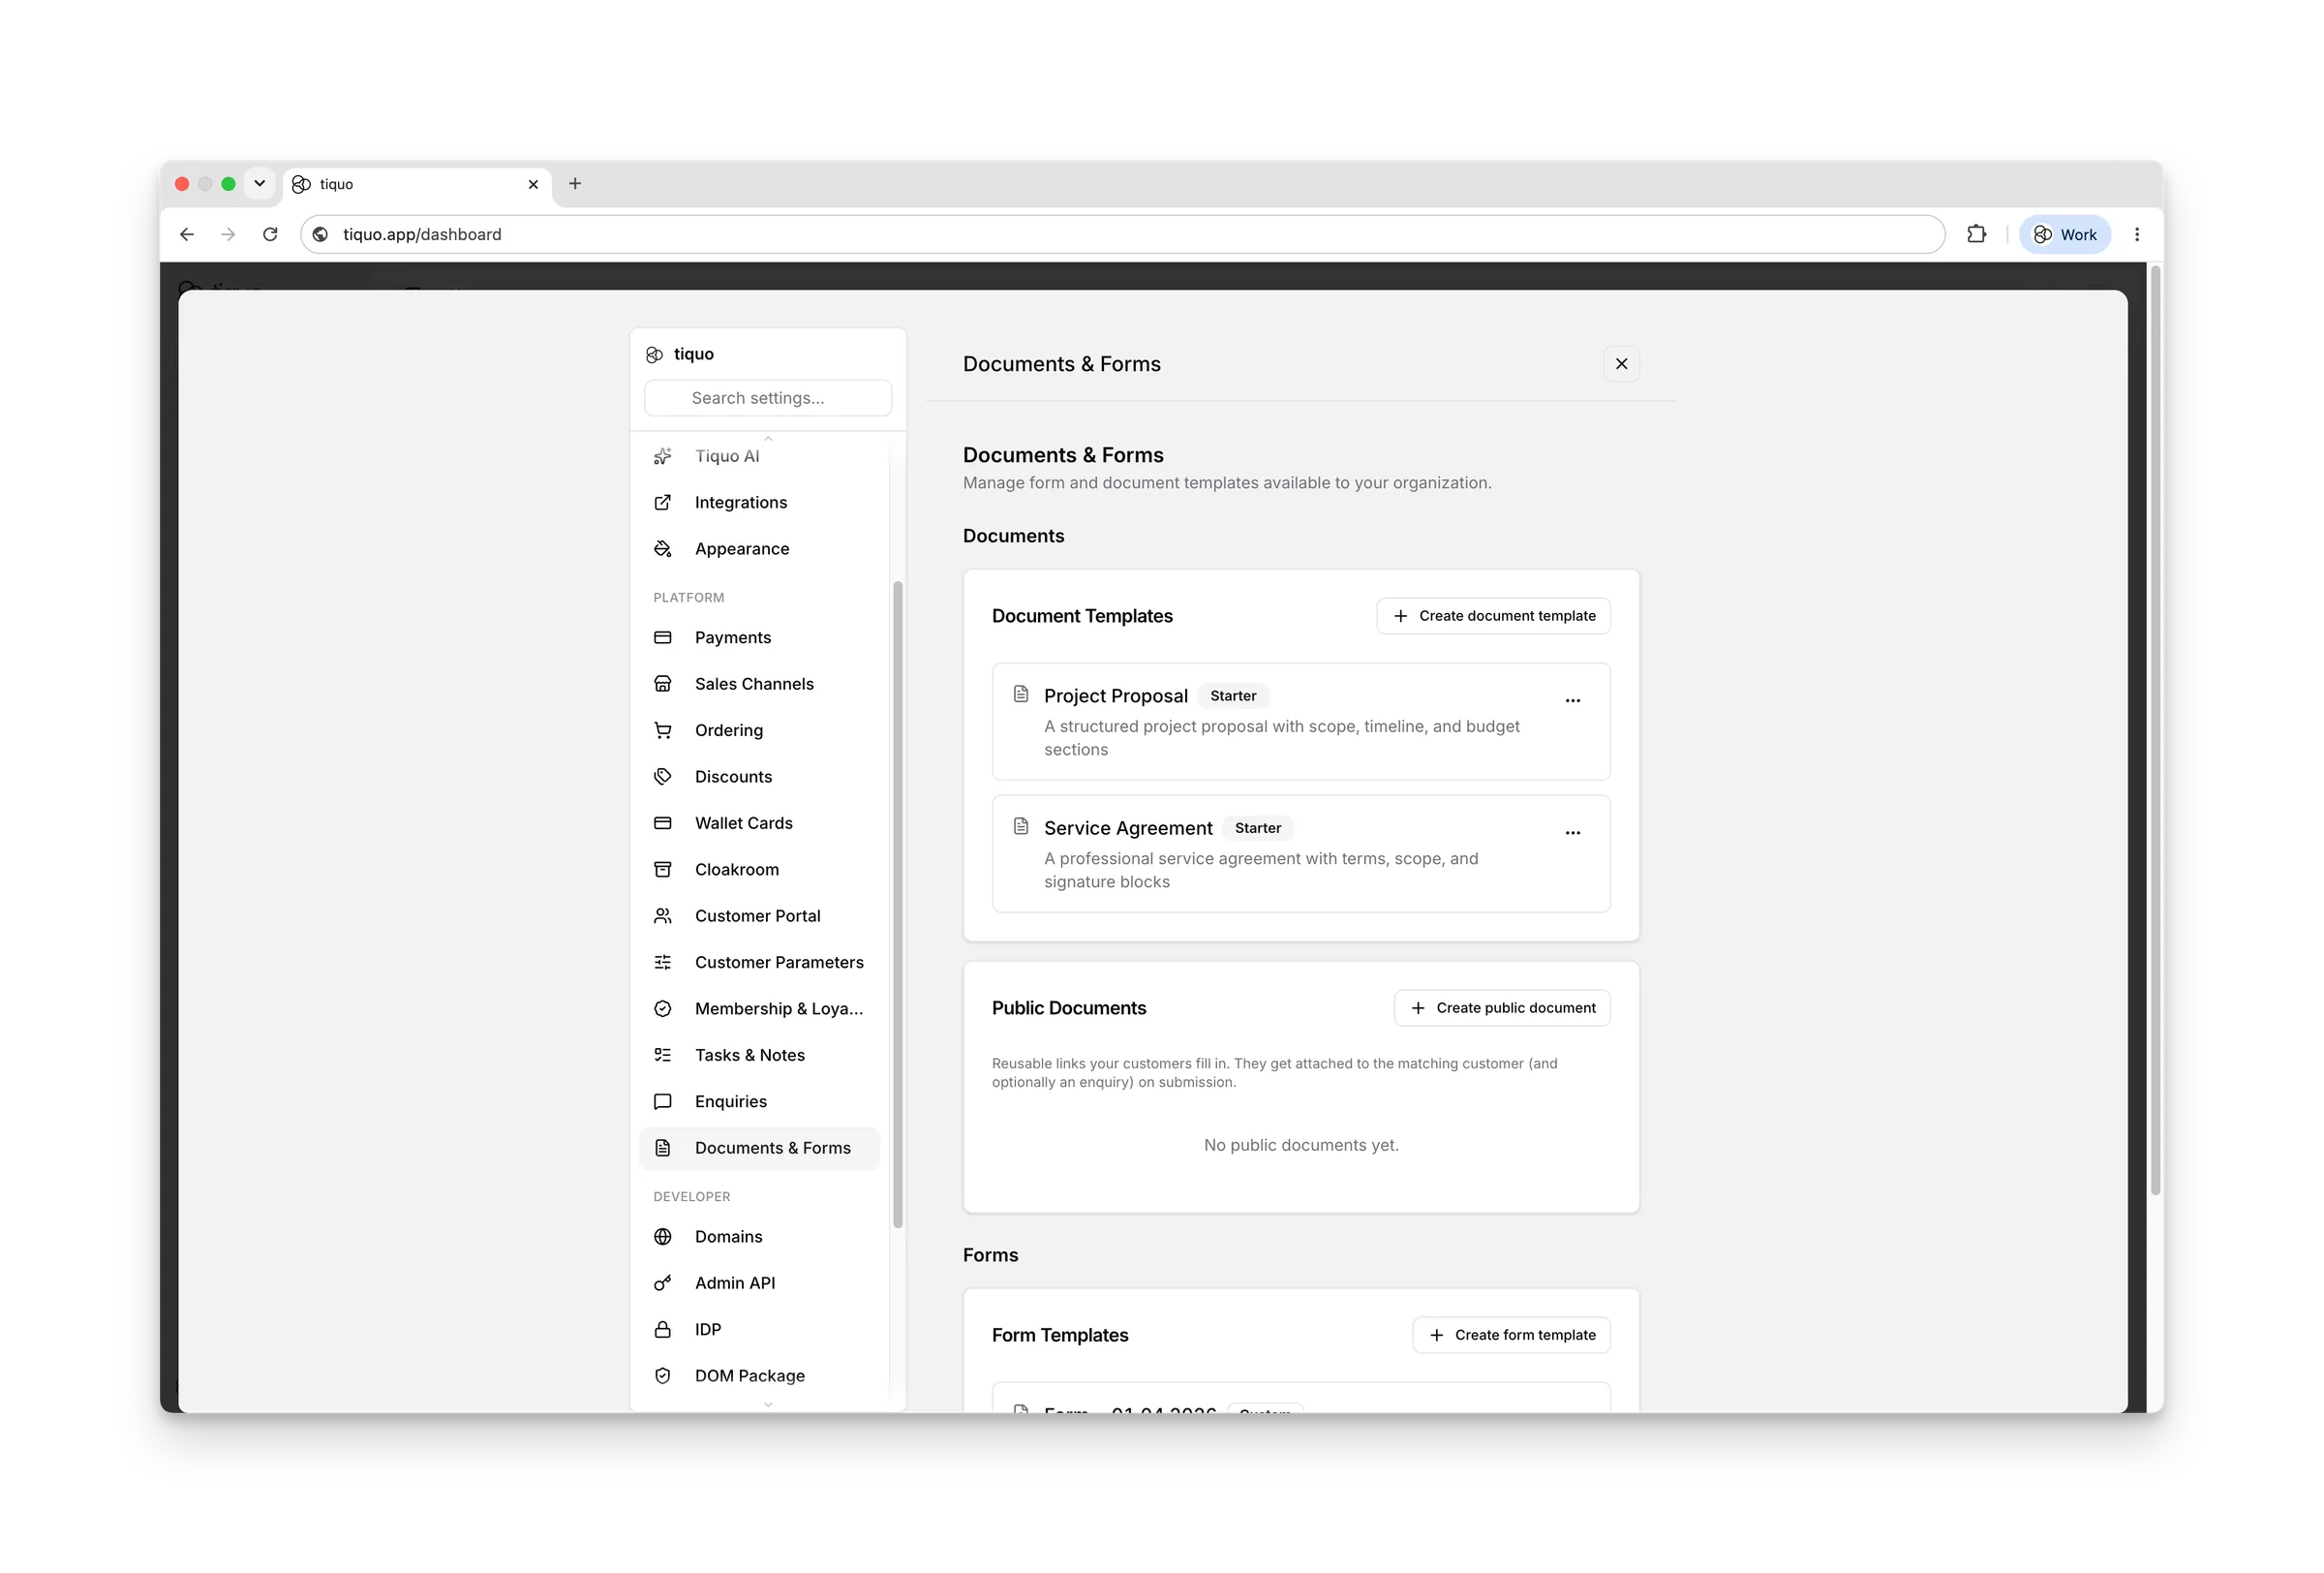
Tiquo document and form templates, including a project proposal and a service agreement

Forms & contracts

Forms, waivers and contracts that file themselves.

Collect answers, photos, signatures and card details once, and every response attaches to the right customer, booking or enquiry.

  • Multi-step forms and waivers
  • Contracts built from templates
  • Card details captured securely
  • Documents on the customer record
  • Sealed, tamper-evident e-signatures
  • Responses that trigger workflows
Learn more
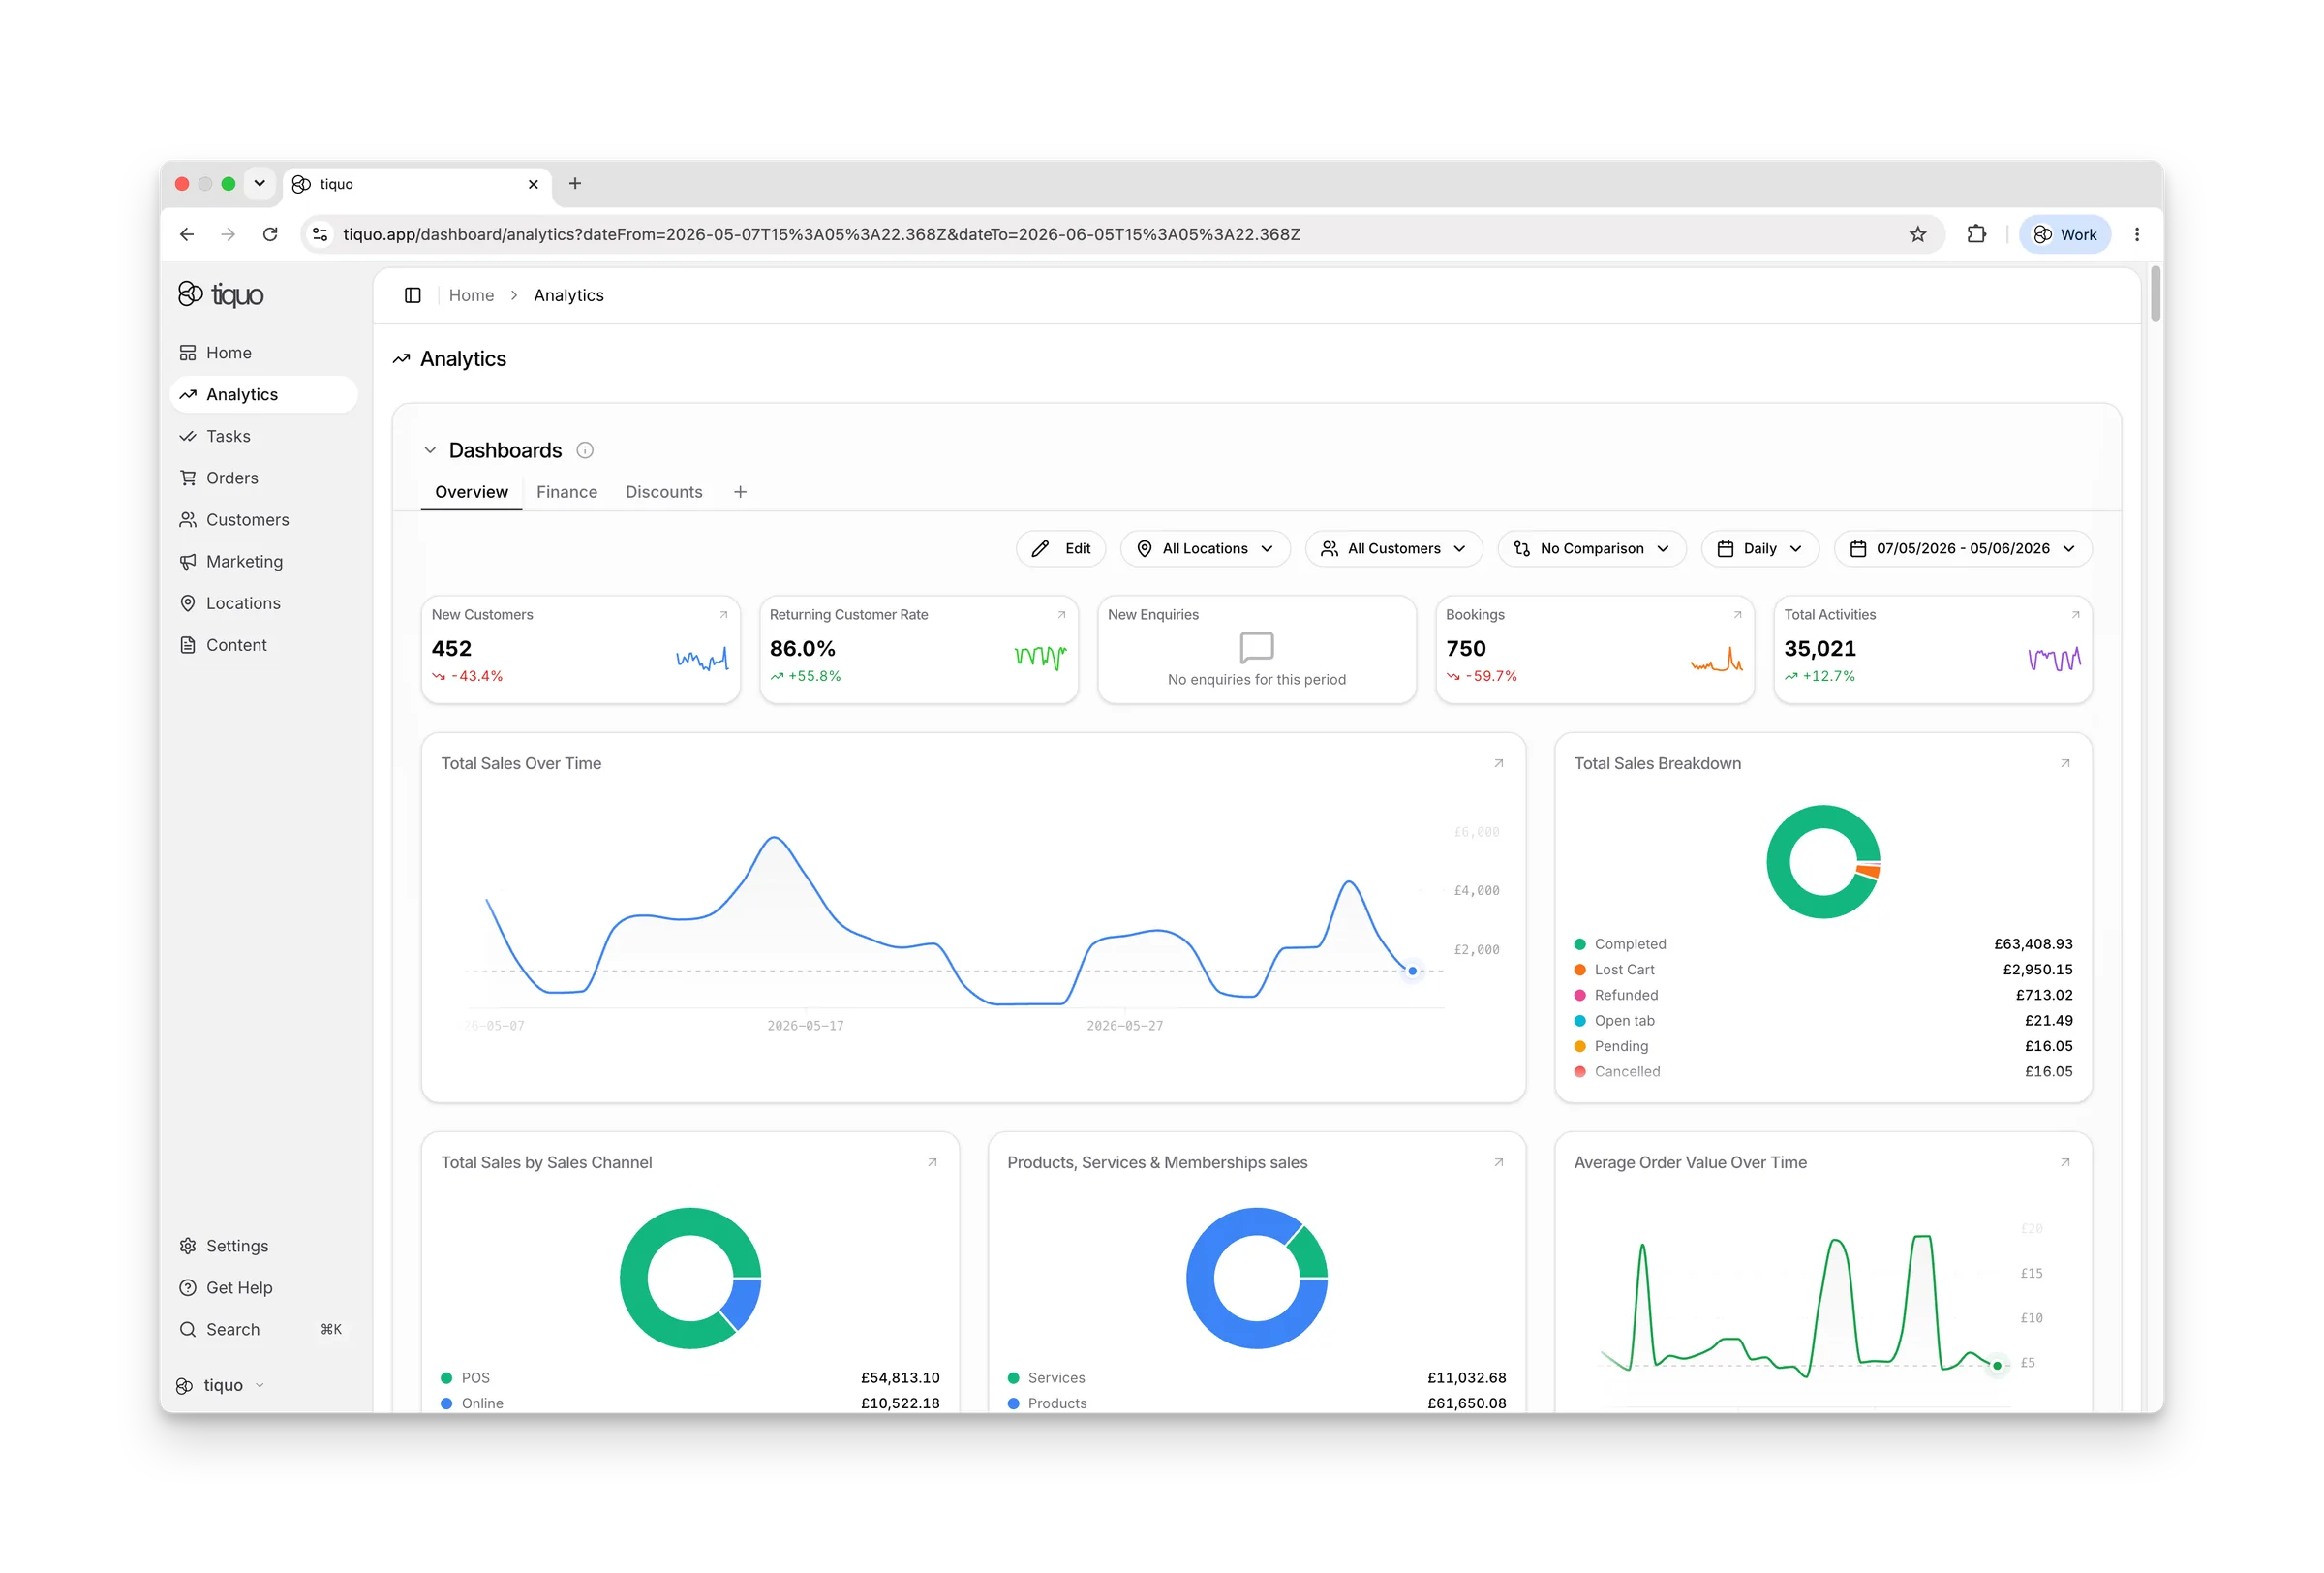
A Tiquo analytics dashboard with sales over time and sales by channel

Reporting

More than 250 analytics cards across the whole business.

Build shared dashboards from live data, compare locations side by side and ask Tiquo AI what changed.

  • Customer and loyalty insight
  • Every location in one view
  • Ask Tiquo AI about your numbers
  • Exports when finance needs them
  • Sales, booking and member reports
  • Live data with no overnight sync
Learn more
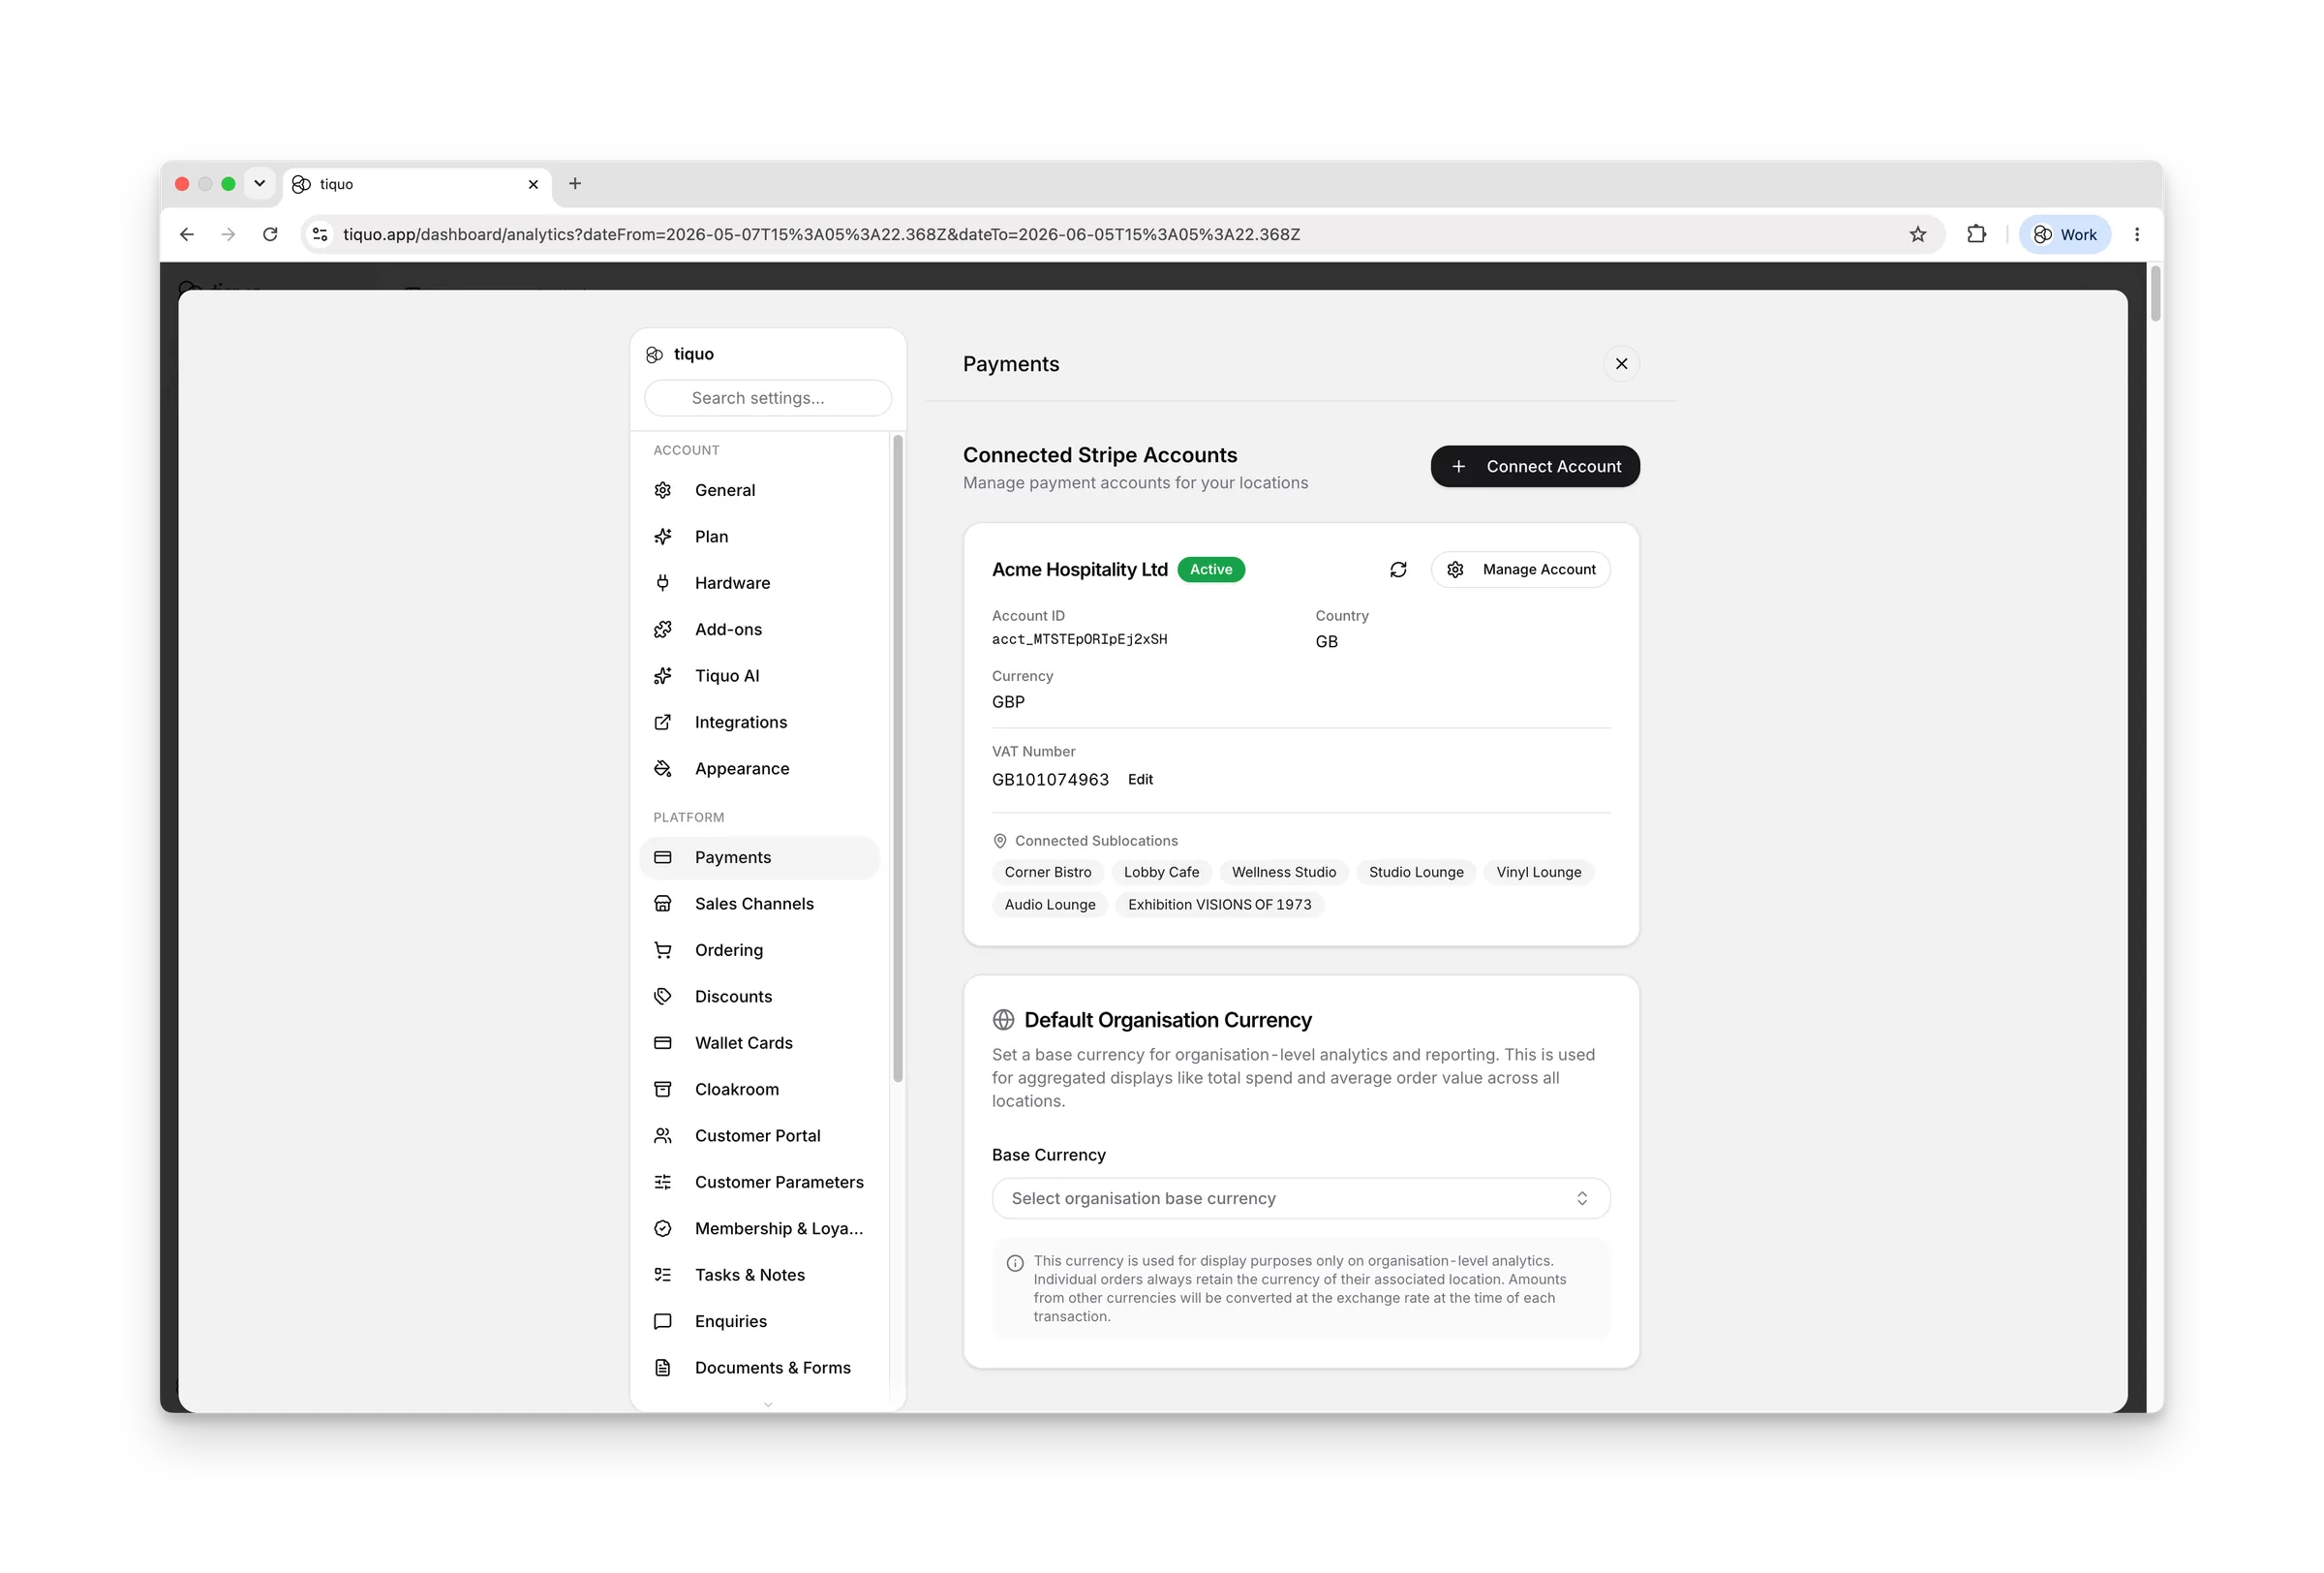
Tiquo payment settings with connected Stripe accounts for several sublocations

Multi-entity

Every brand, venue and legal entity in one account.

Share customers, products and standards across sites while each entity keeps its own payouts, settings and permissions.

  • Locations and sublocations
  • Own payouts and tax ID per entity
  • Reports in one base currency
  • Shared standards, local control
  • Roles and permissions per location
  • One customer record for every site
Learn more

What one platform changes.

Fewer logins for staff, one profile for every guest, and a rollout measured in days rather than quarters.

systems Tiquo can replace, from POS and CRM to wallet cards and KDS
30
is all it can take to go live, with setup, migration and training led by the Tiquo team
5 days
analytics cards for dashboards across sales, bookings, customers and memberships
250+
languages across the staff apps and guest booking pages
30+

Enterprise-ready from day one.

The security and resilience large groups expect, on month-to-month Launch and Scale plans.

Security your IT team can sign off.

Data is protected with 256-bit encryption at rest and in transit, and access is controlled by role and by location.

SOC 2 Type II
Audit in progress
PCI DSS
Level 1 through Stripe
GDPR
UK and EU aligned
  • Access set for each location
  • Audit logs for staff actions
  • Data separated by entity
  • Pen testing and a bug bounty
  • Custom roles, 58 permissions
  • Card data never stored by Tiquo
Read about security

Keeps trading when the Wi-Fi drops.

iPads, iPhones and card terminals on site form an encrypted local mesh. Staff keep taking orders and terminal payments while offline, and everything syncs back automatically when the connection returns.

uptime SLA
99.99%
encryption between devices on the local mesh
AES-256

Ready for your kind of venue.

Start from a setup made for your vertical, then shape the rules, journeys and workflows around the way your team works.

FAQ

Everything, connected.

© 2026 Tiquo. "Tiquo" and the Tiquo logo are registered trademarks of Tiquo Ltd.

GDPR · CCPA · PCI DSS · ICO · Cyber Essentials Certified · EU–US DPF · SOC 2 Type II (in progress) · ISO 27001 (in progress)

Security & Operational

  • 99.99% SLA Uptime
  • AES-256 encryption at rest
  • TLS 1.3 in transit
  • AES-256 / TLS 1.3
  • Perfect Forward Secrecy (PFS)
  • HTTP Strict Transport Security (HSTS)
  • 99.999999999% (11 nines) data durability
  • Automated backups
  • DDoS protection
  • Web Application Firewall (WAF)
  • Zero Trust posture
  • Role-Based Access Control (RBAC)
  • Principle of Least Privilege
  • Secret scanning in CI
  • SBOM generation
  • Dependency supply-chain controls
  • 24/7 infrastructure monitoring
  • GDPR Article 22 safeguards
  • Data Protection Impact Assessments (DPIAs)
  • Records of Processing Activities (ROPA)
  • SAML 2.0 SSO
  • EASIE SSO
  • OAuth 2.0 / OpenID Connect (OIDC)
  • SCIM 2.0 provisioning
  • MFA / 2FA enforcement
  • Responsible disclosure / bug bounty programme

Privacy, Data Protection & Statutory Obligations

  • ICO Registered
  • UK Modern Slavery Act 2015 compliant
  • UK Public Interest Disclosure Act 1998 compliant
  • EU Article 27 Representative appointed (Paris, France)
  • Swiss FADP Article 14 Representative appointed
  • UK GDPR compliant
  • EU GDPR/DSGVO compliant
  • UK Data Protection Act 2018 compliant
  • Swiss revFADP compliant
  • CCPA / CPRA compliant (California)
  • VCDPA compliant (Virginia)
  • CPA compliant (Colorado)
  • CTDPA compliant (Connecticut)
  • TDPSA compliant (Texas)
  • OCPA compliant (Oregon)
  • MCDPA compliant (Montana)
  • FDBR compliant (Florida)
  • ICDPA compliant (Iowa)
  • ICDPA compliant (Indiana)
  • TIPA compliant (Tennessee)
  • DPDPA compliant (Delaware)
  • NJDPA compliant (New Jersey)
  • NHDPA compliant (New Hampshire)
  • NDPA compliant (Nebraska)
  • MCDPA compliant (Minnesota)
  • MODPA compliant (Maryland)
  • KCDPA compliant (Kentucky)
  • RIDTPPA compliant (Rhode Island)
  • Canada PIPEDA compliant
  • Quebec Law 25 compliant
  • Alberta PIPA compliant
  • British Columbia PIPA compliant
  • Singapore PDPA compliant
  • Hong Kong PDPO compliant
  • Brazil LGPD compliant
  • Japan APPI compliant
  • Australia Privacy Act / APPs compliant
  • India DPDPA 2023 compliant
  • Thailand PDPA compliant
  • Malaysia PDPA 2010 (as amended 2024) compliant
  • New Zealand Privacy Act 2020 compliant
  • South Africa POPIA compliant
  • UAE PDPL compliant
  • Mexico LFPDPPP compliant
  • Kenya Data Protection Act 2019 compliant
  • Ghana Data Protection Act 2012 compliant
  • Nigeria NDPA 2023 compliant
  • Indonesia PDP Law 2022 compliant
  • Philippines Data Privacy Act 2012 compliant

Global Fiscal & E-Invoicing

  • EN 16931 - EU e-invoicing core standard
  • UBL 2.1 - Universal Business Language
  • Austria - RKSV
  • Belgium - Peppol BIS 3.0 (B2B)
  • Czechia - fiscalization
  • Croatia - Fiscalization 2.0
  • Denmark - Peppol BIS 3.0 (B2B)
  • France - NF525 / LNE / Infocert, Factur-X / PDP, E-Reporting
  • Germany - KassenSichV / TSE, DSFinV-K, GoBD, E-Rechnung B2B (XRechnung / ZUGFeRD)
  • Hungary - Online Szamla
  • Italy - Scontrino, FatturaPA (via SDI)
  • Lithuania - i.SAF / i.MAS
  • Norway - Peppol BIS 3.0 (B2B), SAF-T
  • Poland - KSeF
  • Portugal - ATCUD/QR, SAF-T PT
  • Slovakia - eKasa
  • Slovenia - fiscalization (davcno potrjevanje)
  • Spain - FacturaE, SII, VeriFactu, TicketBAI
  • Sweden - SKVFS (certified cash registers)
  • Argentina - ARCA (Q4 2026)
  • Australia - Peppol PINT A-NZ (Q4 2026)
  • Brazil - NFe, NFCe, NFSe (Q4 2026)
  • Chile - SII Chile (Q4 2026)
  • Colombia - DIAN (Q4 2026)
  • Finland - Finvoice, TEAPPSXML (Q4 2026)
  • Japan - JP PINT (Peppol) (Q3 2026)
  • Malaysia - Peppol Malaysia (Q4 2026)
  • Mexico - CFDI (Q4 2026)
  • New Zealand - Peppol PINT A-NZ (Q4 2026)
  • Peru - SUNAT (Q4 2026)
  • Romania - Peppol (RO e-invoice) (Q4 2026)
  • Saudi Arabia - ZATCA (Q4 2026)
  • Singapore - Peppol BIS 3.0 (Q4 2026)
  • United Arab Emirates - Peppol (5C) (Q4 2026)

Standards & Frameworks

  • Cyber Essentials Certified
  • SOC 2 Type II - audit in progress
  • ISO/IEC 27001 - audit in progress
  • NIST Cybersecurity Framework - aligned
  • NIST Privacy Framework - aligned
  • NIST SP 800-53 / 800-63 / 800-63B - aligned
  • NIST AI Risk Management Framework - aligned
  • CIS Critical Security Controls / CIS Benchmarks - aligned
  • OWASP ASVS & OWASP Top Ten - aligned
  • ISO 25010 (quality) - aligned
  • ISO 31000 (risk) - aligned
  • ITIL - aligned
  • W3C Web Standards - aligned
  • OpenAPI Standard - aligned
  • DevSecOps practices - aligned
  • ePrivacy Directive - aligned
  • EU Whistleblowing Directive (2019/1937) - aligned

Payments Compliance

  • PCI DSS Level 1
  • PSD2 / Strong Customer Authentication
  • 3D Secure (3DS)
  • EMVCo Level 1 & 2
  • AML / KYC controls
  • Sanctions screening (OFAC, UN, EU, HMT)

International Data Transfer Mechanisms

  • EU-US Data Privacy Framework
  • EU Standard Contractual Clauses (Decision 2021/914) - Modules 2 & 3
  • UK International Data Transfer Agreement (IDTA) + ICO Addendum
  • Swiss FDPIC-recognised transfer mechanisms
  • APEC Cross-Border Privacy Rules (CBPR)

Accessibility Compliance

  • ADA (Americans with Disabilities Act) - aligned
  • European Accessibility Act (EAA) 2025 - aligned
  • WCAG 2.2 - aligned
  • EN 301 549 - aligned
  • WAI-ARIA - aligned

A single platform for hotels, spas, classes, events, restaurants, and more.

Tiquo Ltd
London, UK

LinkedInTop Performer Spring

We use cookies

Choose whether to allow cookies for analytics and advertising. You can accept or decline them. Closing this notice declines them.

Learn more