Paperwork that runs itself.

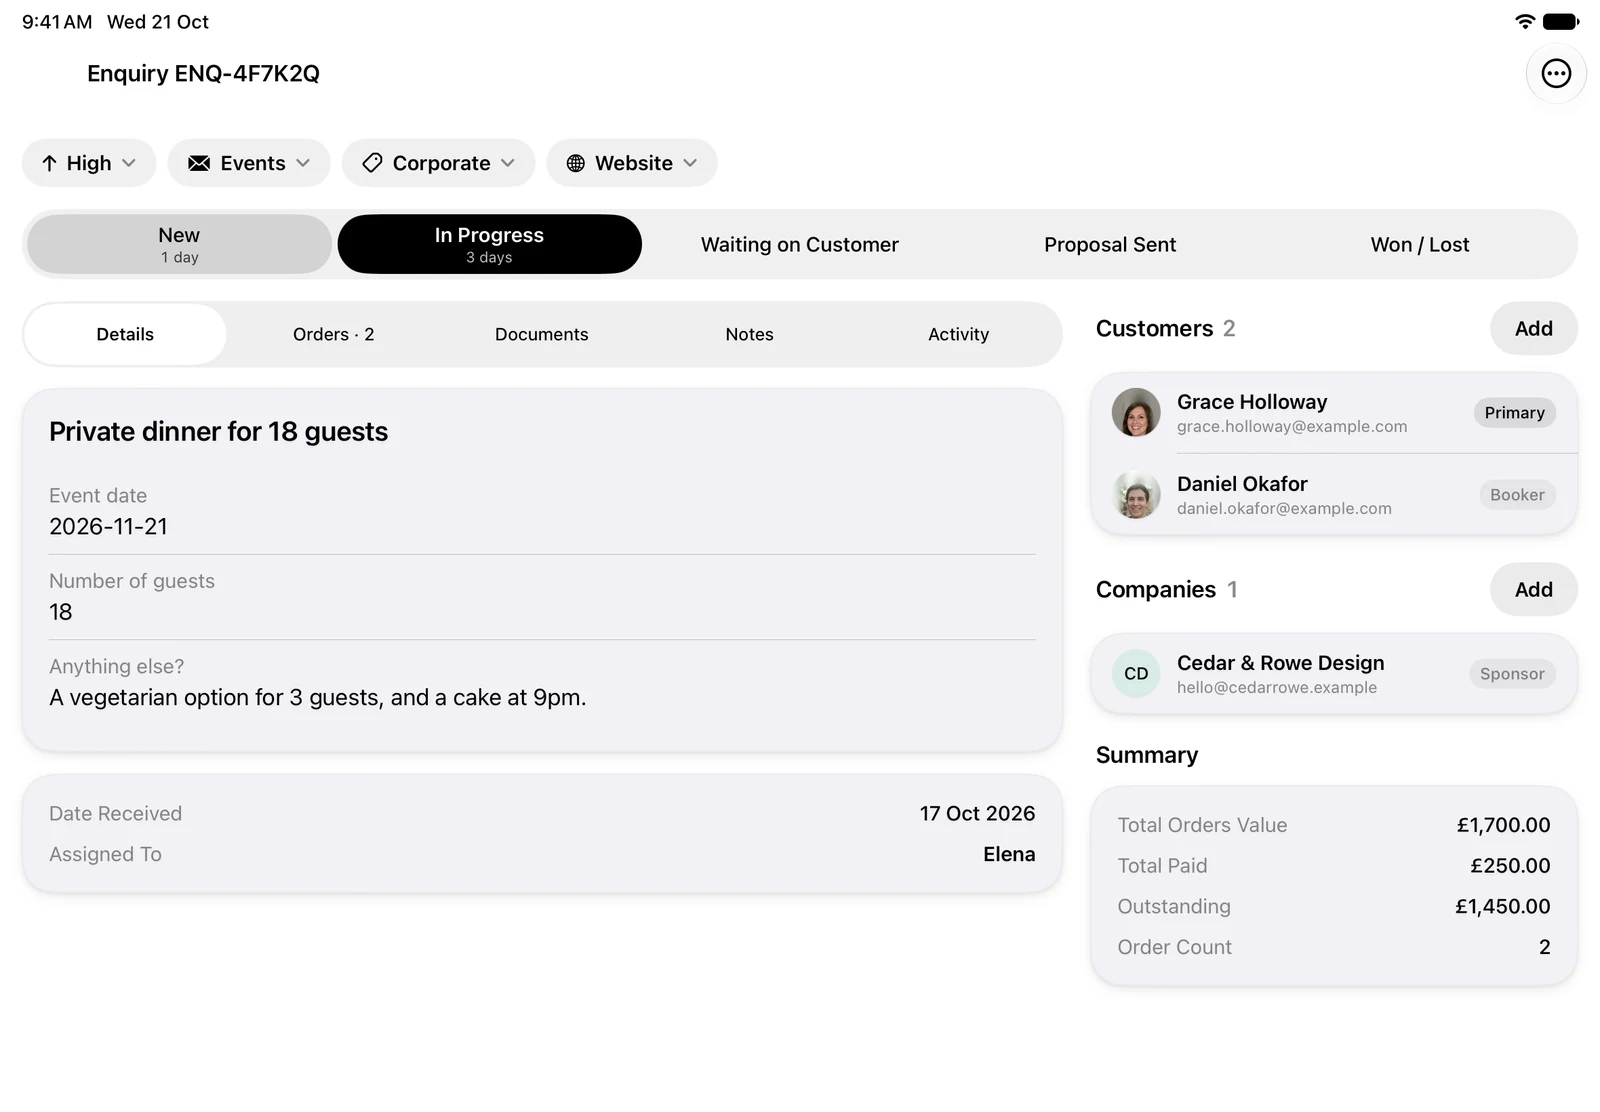
Create multi-step forms and documents that capture structured fields, files, object photos, signatures and payment methods. Use each response to update customer records, create memberships or applications, and route enquiries into the right pipeline.
Forms built for real work.

  1. 01

    Intake forms that capture the right information.

    Create multi-step forms for guests, members or clients. Collect structured answers, files, object photos and the exact information you need before a booking, class, treatment or event takes place.

  2. 02

    Waivers and agreements with built-in signatures.

    Send waivers, consent forms and service agreements digitally, with e-signatures, timestamps and a clear completion history.

  3. 03

    Automatically triggered, never chased.

    Send forms, documents and contracts automatically when a booking is created, updated or rescheduled, so staff don't have to remember each one.

Less paper. More protection.

form completion rate with automated reminders
Up to
95%
reduction in check-in time with pre-completed forms
Up to
80%
of forms stored securely and instantly retrievable
Up to
100%

Filed to the right record.

Documents

Upload FileCreate DocumentCreate Form
Spa intake form
Submitted 14 Oct 2026 • form
Completed
Membership agreement
15 Oct 2026 • Document • Signed on 16 Oct 2026
Signed
2/2 signedEmma MorganLinden House
Treatment consent
16 Oct 2026 • Document • Sent to emma@example.com
Pending signature
0/1 signedEmma Morgan
Passport.pdf
1.2 MB • 2 Oct 2026 • ID Document
Verified

Stored on the customer profile.

All documents are saved against the customer's profile, giving a full history of forms, waivers and agreements across visits and locations.

Filed to enquiries and companies.

Documents can also sit on an enquiry or a company account, so contracts stay with the deal and the business they belong to.

One source of truth.

Store documents securely in Tiquo instead of spreading them across email attachments, shared drives and paper folders.

Flexible logic, full control.

  • Conditional fields and smart logic.

    Show or hide questions based on previous answers, keeping forms short, relevant and easy to complete.

  • Service, location and workflow rules.

    Connect forms to specific services, locations and workflow rules so the right paperwork is applied at the right point in the journey.

  • Permissions and access control.

    Control who can view, edit or manage forms, documents and contracts using role-based permissions.

Secure and compliant by design.

  1. Sent
  2. Opened
  3. Signed
  4. Sealed

Encrypted storage and access controls.

All form data and signed documents are encrypted and protected by role-based access controls.

Audit trails and history.

Track exactly when documents were sent, completed and signed, with full visibility for compliance and accountability.

Built for regulated environments.

Designed to support hospitality, wellness and service businesses where compliance, consent and record-keeping matter.

FAQ

Less paper. More protection.

© 2026 Tiquo. "Tiquo" and the Tiquo logo are registered trademarks of Tiquo Ltd.

GDPR · CCPA · PCI DSS · ICO · Cyber Essentials Certified · EU–US DPF · SOC 2 Type II (in progress) · ISO 27001 (in progress)

Security & Operational

  • 99.99% SLA Uptime
  • AES-256 encryption at rest
  • TLS 1.3 in transit
  • AES-256 / TLS 1.3
  • Perfect Forward Secrecy (PFS)
  • HTTP Strict Transport Security (HSTS)
  • 99.999999999% (11 nines) data durability
  • Automated backups
  • DDoS protection
  • Web Application Firewall (WAF)
  • Zero Trust posture
  • Role-Based Access Control (RBAC)
  • Principle of Least Privilege
  • Secret scanning in CI
  • SBOM generation
  • Dependency supply-chain controls
  • 24/7 infrastructure monitoring
  • GDPR Article 22 safeguards
  • Data Protection Impact Assessments (DPIAs)
  • Records of Processing Activities (ROPA)
  • SAML 2.0 SSO
  • EASIE SSO
  • OAuth 2.0 / OpenID Connect (OIDC)
  • SCIM 2.0 provisioning
  • MFA / 2FA enforcement
  • Responsible disclosure / bug bounty programme

Privacy, Data Protection & Statutory Obligations

  • ICO Registered
  • UK Modern Slavery Act 2015 compliant
  • UK Public Interest Disclosure Act 1998 compliant
  • EU Article 27 Representative appointed (Paris, France)
  • Swiss FADP Article 14 Representative appointed
  • UK GDPR compliant
  • EU GDPR/DSGVO compliant
  • UK Data Protection Act 2018 compliant
  • Swiss revFADP compliant
  • CCPA / CPRA compliant (California)
  • VCDPA compliant (Virginia)
  • CPA compliant (Colorado)
  • CTDPA compliant (Connecticut)
  • TDPSA compliant (Texas)
  • OCPA compliant (Oregon)
  • MCDPA compliant (Montana)
  • FDBR compliant (Florida)
  • ICDPA compliant (Iowa)
  • ICDPA compliant (Indiana)
  • TIPA compliant (Tennessee)
  • DPDPA compliant (Delaware)
  • NJDPA compliant (New Jersey)
  • NHDPA compliant (New Hampshire)
  • NDPA compliant (Nebraska)
  • MCDPA compliant (Minnesota)
  • MODPA compliant (Maryland)
  • KCDPA compliant (Kentucky)
  • RIDTPPA compliant (Rhode Island)
  • Canada PIPEDA compliant
  • Quebec Law 25 compliant
  • Alberta PIPA compliant
  • British Columbia PIPA compliant
  • Singapore PDPA compliant
  • Hong Kong PDPO compliant
  • Brazil LGPD compliant
  • Japan APPI compliant
  • Australia Privacy Act / APPs compliant
  • India DPDPA 2023 compliant
  • Thailand PDPA compliant
  • Malaysia PDPA 2010 (as amended 2024) compliant
  • New Zealand Privacy Act 2020 compliant
  • South Africa POPIA compliant
  • UAE PDPL compliant
  • Mexico LFPDPPP compliant
  • Kenya Data Protection Act 2019 compliant
  • Ghana Data Protection Act 2012 compliant
  • Nigeria NDPA 2023 compliant
  • Indonesia PDP Law 2022 compliant
  • Philippines Data Privacy Act 2012 compliant

Global Fiscal & E-Invoicing

  • EN 16931 - EU e-invoicing core standard
  • UBL 2.1 - Universal Business Language
  • Austria - RKSV
  • Belgium - Peppol BIS 3.0 (B2B)
  • Czechia - fiscalization
  • Croatia - Fiscalization 2.0
  • Denmark - Peppol BIS 3.0 (B2B)
  • France - NF525 / LNE / Infocert, Factur-X / PDP, E-Reporting
  • Germany - KassenSichV / TSE, DSFinV-K, GoBD, E-Rechnung B2B (XRechnung / ZUGFeRD)
  • Hungary - Online Szamla
  • Italy - Scontrino, FatturaPA (via SDI)
  • Lithuania - i.SAF / i.MAS
  • Norway - Peppol BIS 3.0 (B2B), SAF-T
  • Poland - KSeF
  • Portugal - ATCUD/QR, SAF-T PT
  • Slovakia - eKasa
  • Slovenia - fiscalization (davcno potrjevanje)
  • Spain - FacturaE, SII, VeriFactu, TicketBAI
  • Sweden - SKVFS (certified cash registers)
  • Argentina - ARCA (Q4 2026)
  • Australia - Peppol PINT A-NZ (Q4 2026)
  • Brazil - NFe, NFCe, NFSe (Q4 2026)
  • Chile - SII Chile (Q4 2026)
  • Colombia - DIAN (Q4 2026)
  • Finland - Finvoice, TEAPPSXML (Q4 2026)
  • Japan - JP PINT (Peppol) (Q3 2026)
  • Malaysia - Peppol Malaysia (Q4 2026)
  • Mexico - CFDI (Q4 2026)
  • New Zealand - Peppol PINT A-NZ (Q4 2026)
  • Peru - SUNAT (Q4 2026)
  • Romania - Peppol (RO e-invoice) (Q4 2026)
  • Saudi Arabia - ZATCA (Q4 2026)
  • Singapore - Peppol BIS 3.0 (Q4 2026)
  • United Arab Emirates - Peppol (5C) (Q4 2026)

Standards & Frameworks

  • Cyber Essentials Certified
  • SOC 2 Type II - audit in progress
  • ISO/IEC 27001 - audit in progress
  • NIST Cybersecurity Framework - aligned
  • NIST Privacy Framework - aligned
  • NIST SP 800-53 / 800-63 / 800-63B - aligned
  • NIST AI Risk Management Framework - aligned
  • CIS Critical Security Controls / CIS Benchmarks - aligned
  • OWASP ASVS & OWASP Top Ten - aligned
  • ISO 25010 (quality) - aligned
  • ISO 31000 (risk) - aligned
  • ITIL - aligned
  • W3C Web Standards - aligned
  • OpenAPI Standard - aligned
  • DevSecOps practices - aligned
  • ePrivacy Directive - aligned
  • EU Whistleblowing Directive (2019/1937) - aligned

Payments Compliance

  • PCI DSS Level 1
  • PSD2 / Strong Customer Authentication
  • 3D Secure (3DS)
  • EMVCo Level 1 & 2
  • AML / KYC controls
  • Sanctions screening (OFAC, UN, EU, HMT)

International Data Transfer Mechanisms

  • EU-US Data Privacy Framework
  • EU Standard Contractual Clauses (Decision 2021/914) - Modules 2 & 3
  • UK International Data Transfer Agreement (IDTA) + ICO Addendum
  • Swiss FDPIC-recognised transfer mechanisms
  • APEC Cross-Border Privacy Rules (CBPR)

Accessibility Compliance

  • ADA (Americans with Disabilities Act) - aligned
  • European Accessibility Act (EAA) 2025 - aligned
  • WCAG 2.2 - aligned
  • EN 301 549 - aligned
  • WAI-ARIA - aligned

A single platform for hotels, spas, classes, events, restaurants, and more.

Tiquo Ltd
London, UK

LinkedInTop Performer Spring

We use cookies

Choose whether to allow cookies for analytics and advertising. You can accept or decline them. Closing this notice declines them.

Learn more