跳转到主要内容

让每位客人 再次光临。

基于真实的预订、订单、会员和到访数据创建细分受众,发送邮件营销活动,后续跟进交给自动化。无需导出,无需同步,也无需单独的 CRM。
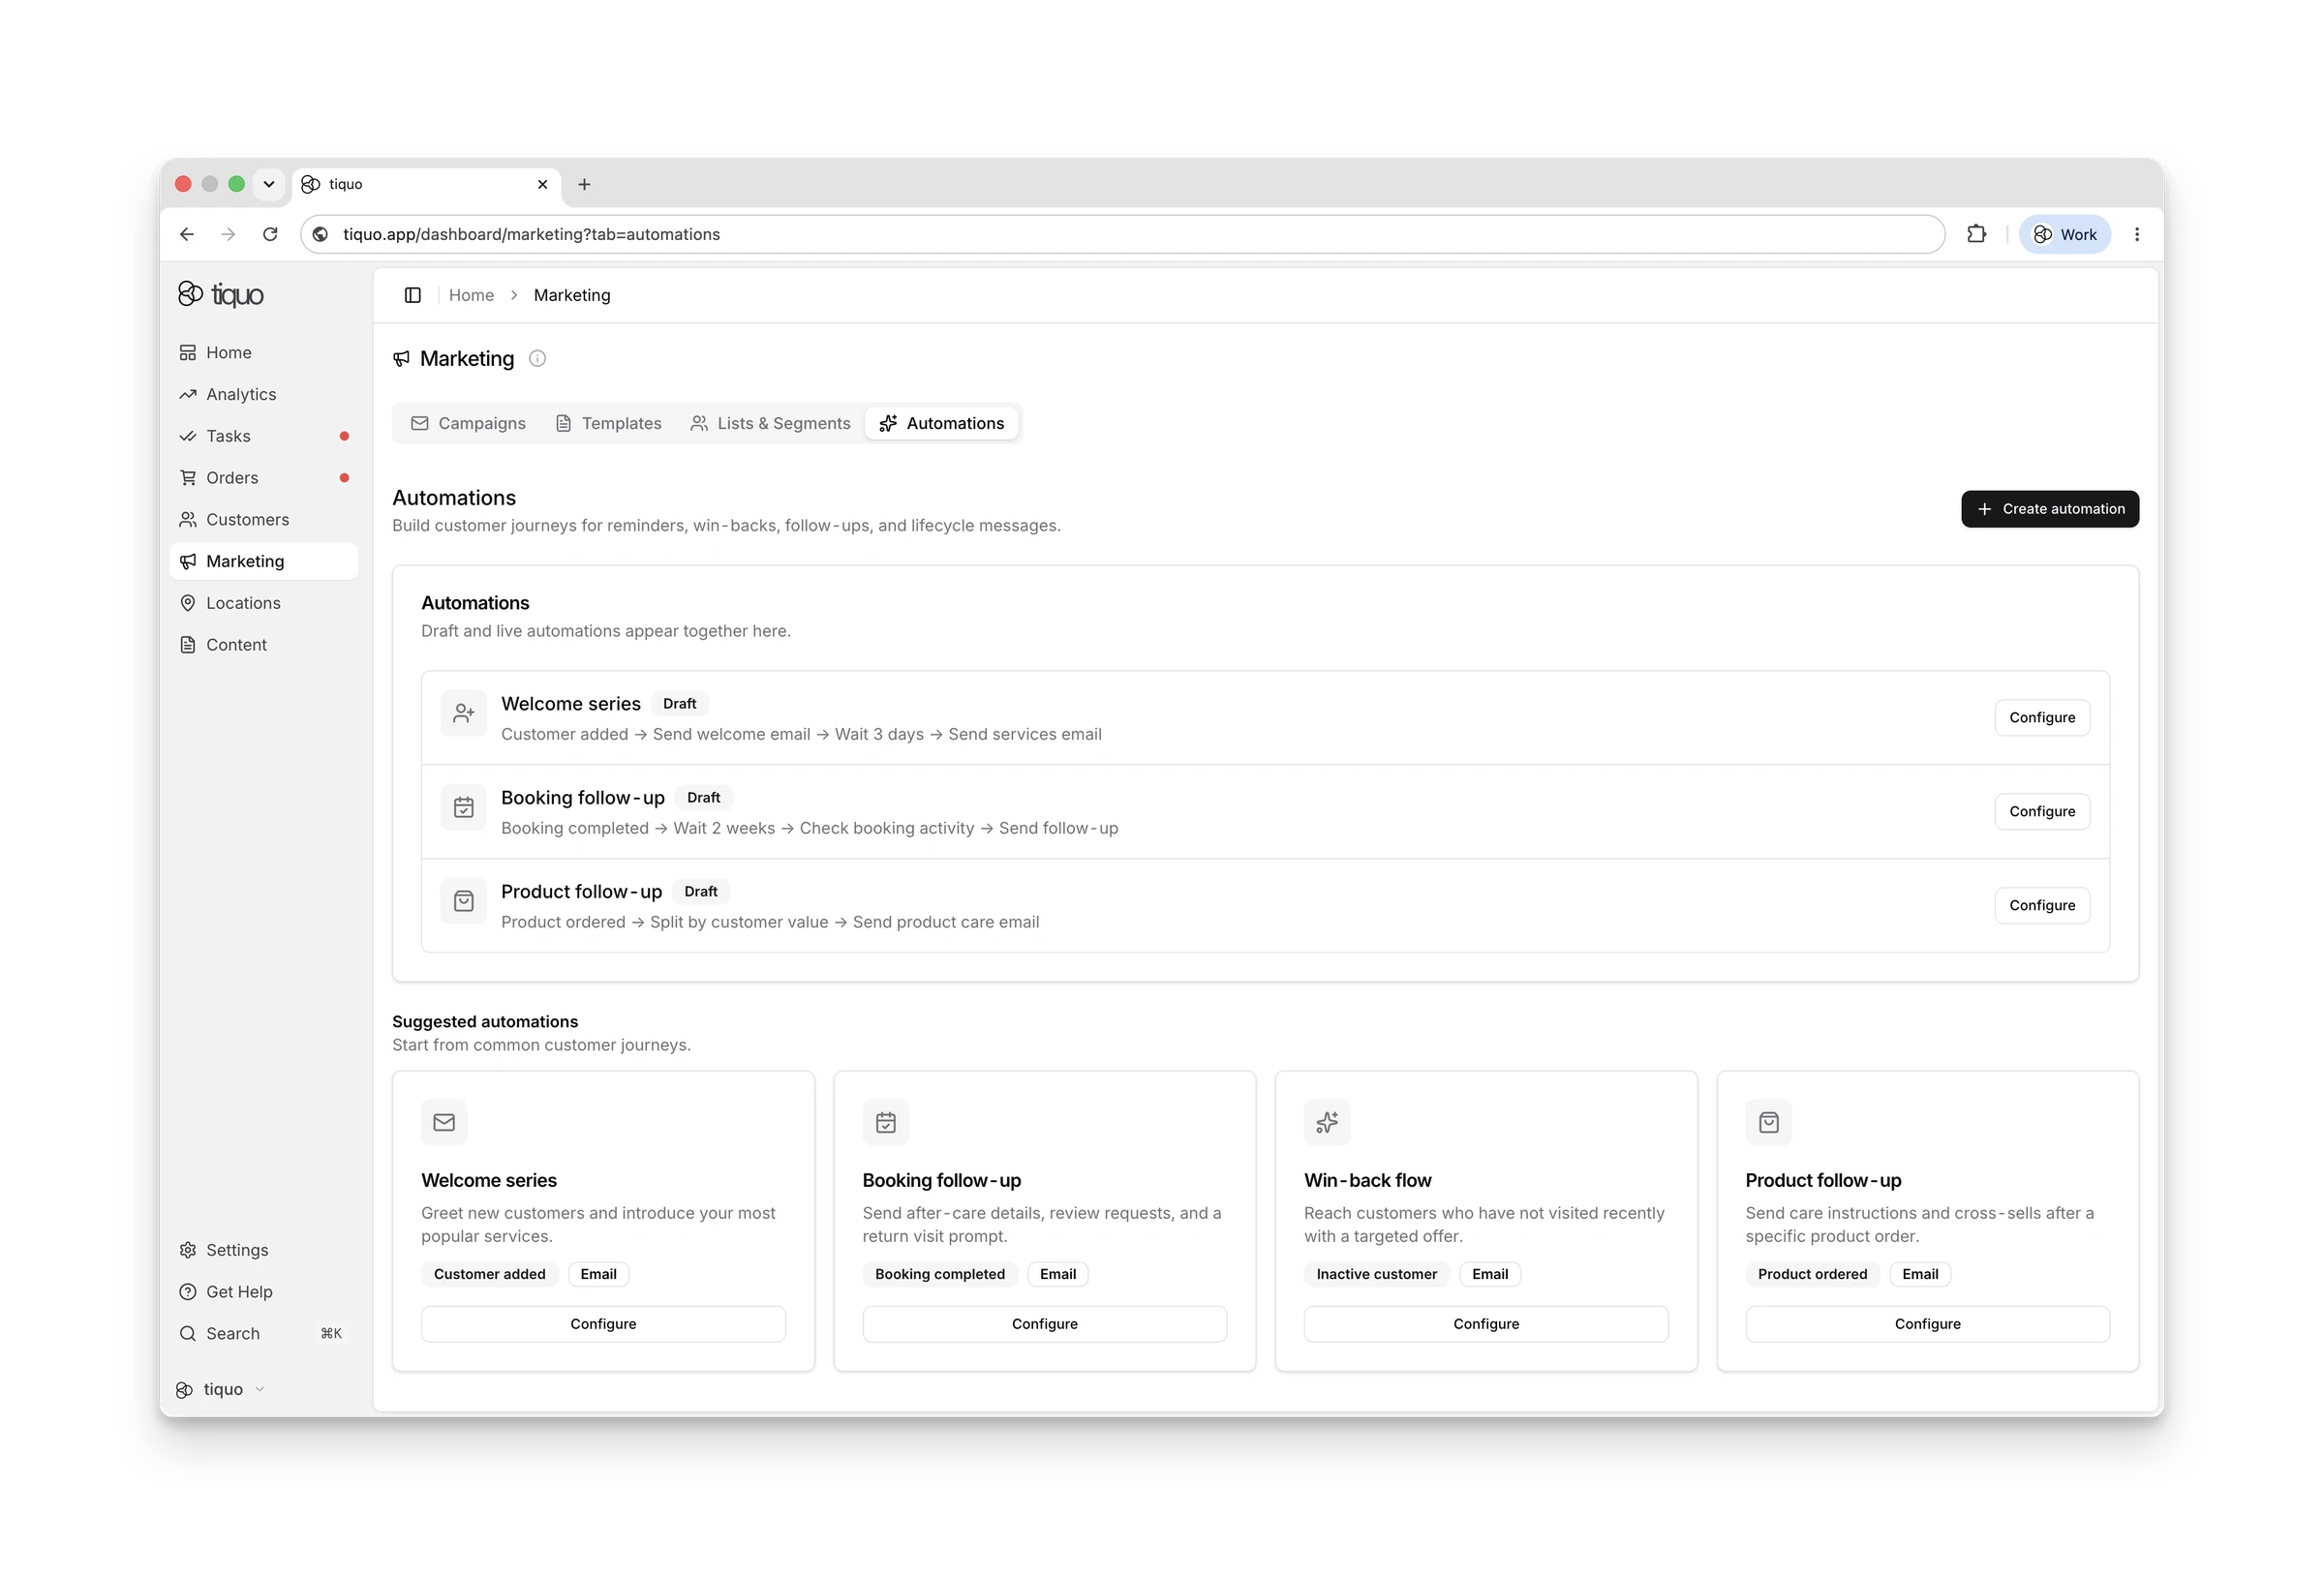
Tiquo marketing automations for welcome series, booking follow-ups and win-backs

用实时客户数据做营销。

选好名单和细分受众,Tiquo 会自动去重,跳过未同意接收的客户,并用姓名、会员日期、积分和消费金额为每封邮件做个性化。

选择受众

选择一个或多个列表或细分来发送此邮件。重复的联系人会自动去除。

收件人列表
列表2

VIP 客人

列表 · 412 位联系人

水疗通讯

列表 · 2,940 位联系人

细分1

90 天未到访

细分 · 1,286 位联系人

已选择 3 个列表

VIP 客人水疗通讯90 天未到访

发送时会在后台核对收件人。只有已订阅的联系人会收到此邮件,在所有已选受众中每个邮箱地址只发送一次。

取消继续
春季菜单
发送
主题:名字,春季菜单上新啦预览:全新春季菜单与会员优惠
Linden House
把春天端上餐桌

名字,您有 积分 积分可在下次到访时使用。

预订餐桌

2026 Linden House. 保留所有权利。

退订

无需代码即可设计

拖放标题、文本、图片、按钮和分栏,可从现成模板开始,也可描述邮件内容,由 AI 起草。

发送前先检查

AI 审核会在发送前标出拼写、语法、垃圾邮件与合规风险、链接格式以及无障碍问题。

效果一目了然

追踪每个营销活动的打开、点击、退信和退订情况,并查看互动趋势和点击最多的链接。

始终最新的细分受众。

可组合 60 多个筛选条件,涵盖到访、消费、预订、会员、忠诚度、咨询以及自定义客户字段。每次发送前都会重新计算细分受众,确保每个营销活动触达当天符合条件的客户。

  • AI 推荐

    Tiquo 会根据您自己客户数据中的规律,推荐值得触达的细分受众。

  • 需要时也能用名单

    导入或手动挑选 VIP 客人、活动嘉宾和抢先体验群组,用文件夹整理,随时导出。

  • 报表中的受众

    将 Analytics 限定到某个名单,查看这部分受众如何预订、购买和消费。

新建细分设置条件,自动将客户归入目标细分
创建细分
筛选条件自动更新
添加条件组
服务记录
按摩添加服务
且最近到访
超过90天前
且已完成预订数
介于5和1,000+次预订之间
且邮件订阅同意
已同意接收邮件
预计结果
符合条件的客户
1,286
位客户
数据约每 5 分钟刷新一次
自动化

自动完成后续跟进。

在预订完成、会员续订、收到表单或购物车被放弃时启动旅程。等待一段时间,按客户后续行为分支,然后执行操作:发送邮件、发放余额或为团队创建任务。

触发器
55
操作
46
  • 上线前试运行
  • 启用前 AI 审核
  • 敏感操作需审批
  • 现成方案快速上手
  • 每个版本均可保存与恢复
  • 任意运行均可重试或重放
已启用 · 3 个步骤 · 运行 128 次
触发器预订已完成子地点:全部子地点
等待等待 2 周然后自动继续
条件检查条件客户已预订服务 · 等于 · 否
否
是
操作发送邮件
  • 模板:预订后回访
  • 类型:营销

客户数 15,000 以内免费。

在客户数据库超过 15,000 位客户之前,邮件营销完全免费。超出后,按您的客户区间收取固定月费。平台方案另行计费。

查看全部价格
客户总数电子邮件营销
0–15,000免费
15,001–25,000US$265.73 每月
90,001–100,000US$863.62 每月
1,000,001+US$6,377.5 每月

内置同意管理。

Tiquo 会在发送时检查同意状态,确保营销活动只送达愿意接收您消息的客户。

  • 邮件和短信分别设置同意
  • 每封邮件都可一键退订
  • 退订会自动更新客户资料
  • 从您已验证的自有域名发送
  • 营销邮件仅发送给已同意的客户
  • 为每位客户提供品牌化的偏好设置页

常见问题

客户数 15,000 以内免费。

© 2026 Tiquo。"Tiquo"和Tiquo标志是Tiquo Ltd的注册商标。

GDPR · CCPA · PCI DSS · ICO · Cyber Essentials Certified · EU–US DPF · SOC 2 Type II (in progress) · ISO 27001 (in progress)

Security & Operational

  • 99.99% SLA Uptime
  • AES-256 encryption at rest
  • TLS 1.3 in transit
  • AES-256 / TLS 1.3
  • Perfect Forward Secrecy (PFS)
  • HTTP Strict Transport Security (HSTS)
  • 99.999999999% (11 nines) data durability
  • Automated backups
  • DDoS protection
  • Web Application Firewall (WAF)
  • Zero Trust posture
  • Role-Based Access Control (RBAC)
  • Principle of Least Privilege
  • Secret scanning in CI
  • SBOM generation
  • Dependency supply-chain controls
  • 24/7 infrastructure monitoring
  • GDPR Article 22 safeguards
  • Data Protection Impact Assessments (DPIAs)
  • Records of Processing Activities (ROPA)
  • SAML 2.0 SSO
  • EASIE SSO
  • OAuth 2.0 / OpenID Connect (OIDC)
  • SCIM 2.0 provisioning
  • MFA / 2FA enforcement
  • Responsible disclosure / bug bounty programme

Privacy, Data Protection & Statutory Obligations

  • ICO Registered
  • UK Modern Slavery Act 2015 compliant
  • UK Public Interest Disclosure Act 1998 compliant
  • EU Article 27 Representative appointed (Paris, France)
  • Swiss FADP Article 14 Representative appointed
  • UK GDPR compliant
  • EU GDPR/DSGVO compliant
  • UK Data Protection Act 2018 compliant
  • Swiss revFADP compliant
  • CCPA / CPRA compliant (California)
  • VCDPA compliant (Virginia)
  • CPA compliant (Colorado)
  • CTDPA compliant (Connecticut)
  • TDPSA compliant (Texas)
  • OCPA compliant (Oregon)
  • MCDPA compliant (Montana)
  • FDBR compliant (Florida)
  • ICDPA compliant (Iowa)
  • ICDPA compliant (Indiana)
  • TIPA compliant (Tennessee)
  • DPDPA compliant (Delaware)
  • NJDPA compliant (New Jersey)
  • NHDPA compliant (New Hampshire)
  • NDPA compliant (Nebraska)
  • MCDPA compliant (Minnesota)
  • MODPA compliant (Maryland)
  • KCDPA compliant (Kentucky)
  • RIDTPPA compliant (Rhode Island)
  • Canada PIPEDA compliant
  • Quebec Law 25 compliant
  • Alberta PIPA compliant
  • British Columbia PIPA compliant
  • Singapore PDPA compliant
  • Hong Kong PDPO compliant
  • Brazil LGPD compliant
  • Japan APPI compliant
  • Australia Privacy Act / APPs compliant
  • India DPDPA 2023 compliant
  • Thailand PDPA compliant
  • Malaysia PDPA 2010 (as amended 2024) compliant
  • New Zealand Privacy Act 2020 compliant
  • South Africa POPIA compliant
  • UAE PDPL compliant
  • Mexico LFPDPPP compliant
  • Kenya Data Protection Act 2019 compliant
  • Ghana Data Protection Act 2012 compliant
  • Nigeria NDPA 2023 compliant
  • Indonesia PDP Law 2022 compliant
  • Philippines Data Privacy Act 2012 compliant

Global Fiscal & E-Invoicing

  • EN 16931 - EU e-invoicing core standard
  • UBL 2.1 - Universal Business Language
  • Austria - RKSV
  • Belgium - Peppol BIS 3.0 (B2B)
  • Czechia - fiscalization
  • Croatia - Fiscalization 2.0
  • Denmark - Peppol BIS 3.0 (B2B)
  • France - NF525 / LNE / Infocert, Factur-X / PDP, E-Reporting
  • Germany - KassenSichV / TSE, DSFinV-K, GoBD, E-Rechnung B2B (XRechnung / ZUGFeRD)
  • Hungary - Online Szamla
  • Italy - Scontrino, FatturaPA (via SDI)
  • Lithuania - i.SAF / i.MAS
  • Norway - Peppol BIS 3.0 (B2B), SAF-T
  • Poland - KSeF
  • Portugal - ATCUD/QR, SAF-T PT
  • Slovakia - eKasa
  • Slovenia - fiscalization (davcno potrjevanje)
  • Spain - FacturaE, SII, VeriFactu, TicketBAI
  • Sweden - SKVFS (certified cash registers)
  • Argentina - ARCA (Q4 2026)
  • Australia - Peppol PINT A-NZ (Q4 2026)
  • Brazil - NFe, NFCe, NFSe (Q4 2026)
  • Chile - SII Chile (Q4 2026)
  • Colombia - DIAN (Q4 2026)
  • Finland - Finvoice, TEAPPSXML (Q4 2026)
  • Japan - JP PINT (Peppol) (Q3 2026)
  • Malaysia - Peppol Malaysia (Q4 2026)
  • Mexico - CFDI (Q4 2026)
  • New Zealand - Peppol PINT A-NZ (Q4 2026)
  • Peru - SUNAT (Q4 2026)
  • Romania - Peppol (RO e-invoice) (Q4 2026)
  • Saudi Arabia - ZATCA (Q4 2026)
  • Singapore - Peppol BIS 3.0 (Q4 2026)
  • United Arab Emirates - Peppol (5C) (Q4 2026)

Standards & Frameworks

  • Cyber Essentials Certified
  • SOC 2 Type II - audit in progress
  • ISO/IEC 27001 - audit in progress
  • NIST Cybersecurity Framework - aligned
  • NIST Privacy Framework - aligned
  • NIST SP 800-53 / 800-63 / 800-63B - aligned
  • NIST AI Risk Management Framework - aligned
  • CIS Critical Security Controls / CIS Benchmarks - aligned
  • OWASP ASVS & OWASP Top Ten - aligned
  • ISO 25010 (quality) - aligned
  • ISO 31000 (risk) - aligned
  • ITIL - aligned
  • W3C Web Standards - aligned
  • OpenAPI Standard - aligned
  • DevSecOps practices - aligned
  • ePrivacy Directive - aligned
  • EU Whistleblowing Directive (2019/1937) - aligned

Payments Compliance

  • PCI DSS Level 1
  • PSD2 / Strong Customer Authentication
  • 3D Secure (3DS)
  • EMVCo Level 1 & 2
  • AML / KYC controls
  • Sanctions screening (OFAC, UN, EU, HMT)

International Data Transfer Mechanisms

  • EU-US Data Privacy Framework
  • EU Standard Contractual Clauses (Decision 2021/914) - Modules 2 & 3
  • UK International Data Transfer Agreement (IDTA) + ICO Addendum
  • Swiss FDPIC-recognised transfer mechanisms
  • APEC Cross-Border Privacy Rules (CBPR)

Accessibility Compliance

  • ADA (Americans with Disabilities Act) - aligned
  • European Accessibility Act (EAA) 2025 - aligned
  • WCAG 2.2 - aligned
  • EN 301 549 - aligned
  • WAI-ARIA - aligned

在一个平台管理酒店、水疗、课程、活动和餐厅业务。

Tiquo Ltd
英国伦敦

LinkedInTop Performer Spring

我们使用 Cookie

您可以接受或拒绝用于分析和广告的 Cookie。关闭此提示也会拒绝这些 Cookie。

了解更多